BETA nonprofit public democratic european moderated

The Shadowserver Foundation

4 posts

The Shadowserver Foundation

Mentions and quotes

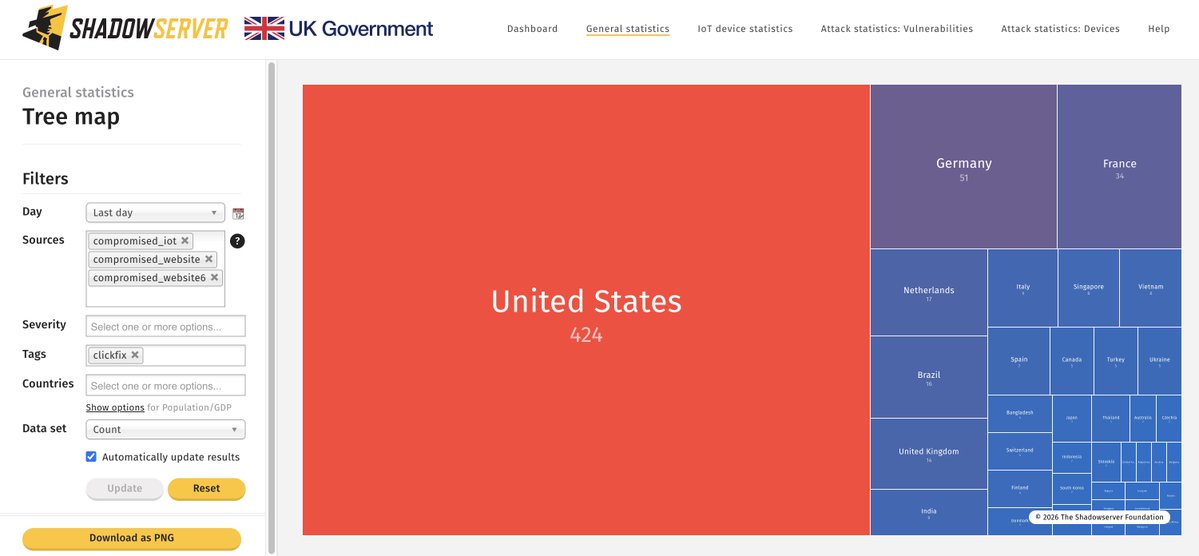
We added a feed of IPs/websites with ClickFix/ClearFake injected code in our Compromised Website reporting, tagged as 'clickfix'. Visitors of the website get tricked to install malware when injected JavaScript executes. If you receive an alert review for root cause of compromise! https://t.co/pQllnpPkLy -
@Europol @MicrosoftDCU nCSIRT-only Tycoon 2FA Domains Special Report run 2026-03-04 (historical C2/panel/infra domains) link: https://t.co/DiQBcmjzLZ -

Compromised Website Report (now with ClickFix data!): https://t.co/D1KZAGvfTr Dashboard World Map view of infected IPs: https://t.co/czz0s9XsQp Dashboard Tree Map view of infected IPs: https://t.co/WMiAnd22O8 -

657 instances shared for 2026-03-14. We expect to increase the volume of the feed in the future! We would like to thank our Alliance partners and @ValidinLLC for the collaboration making this possible! Background on investigating ClickFix/ClearFake: https://t.co/UY8NFEKr1C -