WRLD

Search

#Hacking
Roman M🐦 8h

Roman M🐦 wrote that hackers from North Korea were seeking jobs through LinkedIn and VPNs and subsequently infiltrating American and European companies, from which they stole data and cryptocurrencies that he said were sent to Pyongyang. He added that their Dutch counterpart turned on the camera and saw them in North Korean army uniforms; he described their expression as empty. #kyberbezpečnost #hacking #VPN (translated)
1816
Peter Jukes 2d

The only other logical explanation for Trump going all in to support Putin right now (apart from the Kompromat/Krasnov theory) is that he needs Russian hacking/information warfare help in the mid terms. Which just underlies how much they helped in the past

1937
La Libre.be 2d

In Belgium, more cyber incidents have been reported this year than in all of 2025, a situation highlighted by the recent hacking of refrigerators in French retail, where tons of food became unconsumable due to attacks possibly linked to foreign hackers. #cybersécurité #piratage #grandedistribution (translated)
www.lalibre.be
Frigos piratés dans la grande distribution : une culture de la sécurité à ancrer
2561
SaxX ¯\_(ツ)_/¯ 3d

SaxX reported that a hacker had accessed the Danish central registry of persons, the CPR, and retrieved data associated with about 8.8 million identification numbers. According to him, these concerned living people, deceased individuals, or those who had gone abroad, and included names, addresses, and personal numbers. The author clarified that the intrusion did not directly target the Danish state, but Pays ApS, an IT company in Odense that had legal access to the registry to verify its clients' files. He indicated that the company had only two employees. Citing the newspaper Politiken, he wrote that at least three of its accounts used the password "123456", including that of the administrator. According to SaxX's account, the hacker allegedly used a leaked password from a former employee, maintained access for 21 days and 17 hours, and carried out about 14 million automated searches between September 10 and 20. The hacker also claimed that his data recovery program had been written by an AI, that he had no particular technical skills, and that he did not intend to sell or publish the data. SaxX stated that the intrusion was only discovered on October 2, after an official noticed an abnormally high bill, as searches in the registry are paid. He added that the Minister of Digital Affairs had described the incident as "deeply serious." The author also reported that the number of citizens who activated a credit fraud alert had risen from about 250,000 to nearly 970,000 in one week. According to him, the CPR had then reminded the security rules to 1,039 companies that had access to the registry, including banks, telecom operators, law firms, unions, and insurers. Finally, SaxX estimated that the incident demonstrated the risks associated with access granted to private providers, as several African states digitized their civil registries. #Cybersécurité #Hacking #Danemark (translated)
3458
Idriss J. Aberkane Ph.D x3 4d

The author claimed that it was not a joke and that a password "123456" had allowed a hacker to compromise the identity files of 8.8 million Danes. #cybersécurité #hacking #motdepasse #DK (translated)
3814
Kultur 4d

Culture indicated that the hacker CYBERLEEK had announced the end of the leaks about GTA VI. According to him, CYBERLEEK had, however, activated a mechanism that would release the entire game and spoilers if he were stopped by the authorities. https://t.co/Swzj17xQNl #GTA6 #Hacking #JeuxVideo (translated)
3150
TV2 ØSTJYLLAND 7d

18-year-old Jonas from Randers is striving to win European Championship gold in hacking. (translated)
www.tv2ostjylland.dk
18-årig fra Randers jagter EM-guld i hacking
2494
MΛRC VIDΛL 7d

The author noted that Germany had opened, through HackerOne and before its deployment, the d-you digital identity wallet and the EUDI ecosystem to external hackers to detect security flaws. https://t.co/wdRIqrmK9M https://t.co/NnPgEIgauo #Ciberseguridad #Hacking #IdentidadDigital #DE (translated)
2954
Bild 1w

Security researchers demonstrated at the Pwn2Own Ireland 2026 hacking competition that the Samsung Galaxy S26 can be hacked remotely via a crafted email and four previously unknown security vulnerabilities. #Samsung #Sicherheit #Hacking (translated)
www.bild.de
Schwachstelle bei Samsung - Galaxy S26 per E-Mail gehackt!
1486
Apollo News 2w

Apollo News reported that Correctiv had access to sensitive editorial data from Nius and used it for its own research. According to Nius, the data came from an illegal hacking attack. Correctiv denied having been involved in obtaining the data set. https://t.co/E9nlJCZfSg #Journalismus #Datenschutz #Hacking (translated)

2975
Gerd Leonhard 2w

The author recommended a Bruce Schneier video as essential viewing on the future of AI, hacking and related topics.

Niebezpiecznik 2w

Niebezpiecznik wrote that Wakacje.pl informed customers about a breach in which the perpetrators had obtained their personal data, including passport information. The author added that a joke about an attack targeting an industry other than healthcare would not be funny. https://t.co/BoylpFoj3s #cyberbezpieczeństwo #hacking #daneosobowe (translated)

12313
Stefania Maurizi 2w

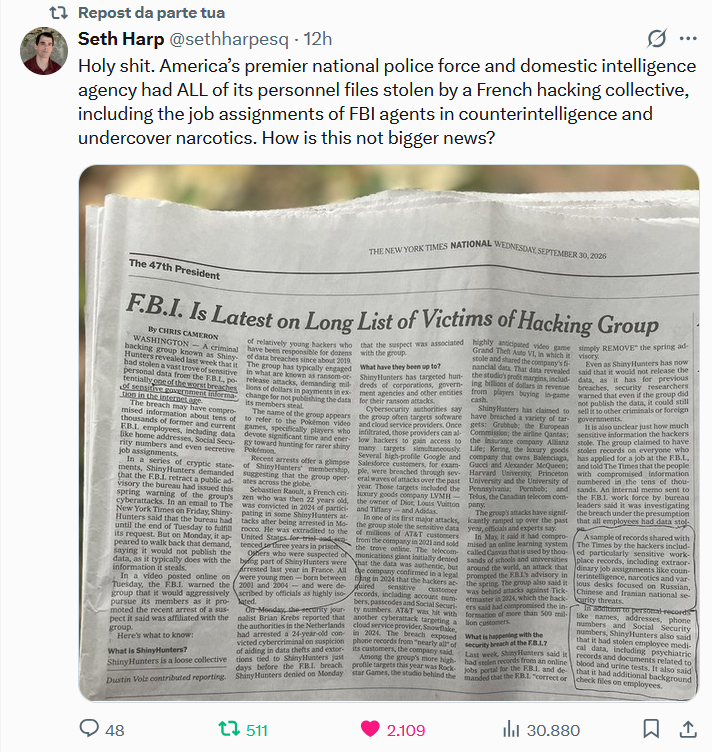
The author said they had been unable to reach the FBI’s FOIA email for the past two weeks and were unsure whether it was related to a major hack targeting the FBI, allegedly carried out by the French hacking collective ShinyHunters. https://t.co/HKobwXwMDA #FBI #Hacking #FOIA #FR

D
der Standard 2w

OpenAI has fired three employees who were involved in the processing of independent hacking activities related to Artificial Intelligence, as they violated internal rules regarding the handling of confidential information. #KünstlicheIntelligenz #OpenAI #ChatGPT (translated)

www.derstandard.at
ChatGPT-Entwickler OpenAI entlässt nach KI-Enthüllungen drei Mitarbeiter
1498
newsORF.at 2w

OpenAI has dismissed three employees who were involved in independent hacking activities related to their AI, as they violated internal rules regarding the handling of confidential information. #OpenAI #KünstlicheIntelligenz #Datenschutz (translated)

orf.at
OpenAI entlässt drei Mitarbeiter nach KI-Enthüllungen
1729
A
AD 2w

The Dutch hacker 'Archduke' from the hackers group KillSec, Fouad E., has been arrested in the United Kingdom as part of an international operation following his involvement in multiple cyberattacks and data thefts. #KillSec #cybercriminaliteit #hacking (translated)

www.ad.nl
Nederlandse hacker ‘Archduke’ van KillSec opgepakt in Verenigd Koninkrijk bij grote internationale operatie
1498
Daniel Dočekal 3w

Nedělní #TYDEN ::: AI kill switch?! Agent OpenAI hackoval v Austrálii. Média ztrácejí návštěvnost Digitální úklid. Téma: Datová centra. Trump stále válčí s médii. ShinyHunters hackli FBI. #free https://t.co/A1NUPr4cps #full https://t.co/XVcsnNObMJ #AI #hacking #media #AU

Chris Avramidis 3w

🇪🇺 Στο Ευρωπαϊκό Κοινοβούλιο κατατέθηκε τροπολογία που ζητούσε να καταδικαστεί κάθε παρέμβαση των ισραηλινών Αρχών στις δημοκρατικές διαδικασίες. Όλοι οι ευρωβουλευτές της Νέας Δημοκρατίας ψήφισαν κατά. Και αυτό ενώ υπάρχουν ήδη πολύ ανησυχητικά γεγονότα για τη δημοκρατία. 🇫🇷 Στη Γαλλία, ισραηλινοί δρώντες προσπάθησαν να επηρεάσουν εκλογές, σύμφωνα με την αρμόδια κρατική υπηρεσία. Στόχευσαν το κόμμα που αντιτίθεται στη γενοκτονία στην #Παλαιστίνη. 🇺🇸 Στις ΗΠΑ, το φιλοϊσραηλινό AIPAC έχει δαπανήσει δεκάδες εκατομμύρια δολάρια επηρεάζοντας εκλογικές αναμετρήσεις. 🇬🇷 Αλλά αυτά δεν είναι γνωστά μόνο στο εξωτερικό. Υπάρχει και η Ελλάδα. Ο επικεφαλής την περιβόητης Ισραηλινής ομάδας Team Jorge που προσέφερε υπηρεσίες χειραγώγησης της κοινής γνώμης και hacking είχε δηλώσει: «έχουμε ομάδα στην Ελλάδα». Η Haaretz είχε αποκαλύψει συναντήσεις Ισραηλινών ειδικών με στελέχη που συνδέονταν με την προεκλογική καμπάνια της Νέας Δημοκρατίας. Το δημοσίευμα αναφερόταν σε επανειλημμένα ταξίδια στην Ελλάδα, συναντήσεις αλλά και αμοιβή, σύμφωνα με μία πηγή. Με όλα αυτά γνωστά, λοιπόν, ρωτήσαμε τον κυβερνητικό εκπρόσωπο: Γιατί όλοι οι ευρωβουλευτές της Νέας Δημοκρατίας ψήφισαν κατά; Θεωρεί η κυβέρνηση ότι οι παρεμβάσεις ξένων κρατών στις δημοκρατικές διαδικασίες δεν αποτελούν πρόβλημα όταν προέρχονται από ισραηλινούς δρώντες; 🤷 Ο Παύλος Μαρινάκης απάντησε ότι οι παρεμβάσεις γενικά αποτελούν πρόβλημα. Για το συγκεκριμένο «όχι» της ΝΔ όμως είπε ότι δεν γνώριζε τον λόγο και ότι θα ρωτούσε την ευρωομάδα της Νέας Δημοκρατίας. Και στη συνέχεια προσπάθησε να εμφανίσει περίπου ως παράλογη την ερώτησή μας. Μας είπε ότι οι ευρωβουλευτές είναι ελεύθεροι να ψηφίζουν, ότι ο ίδιος δεν τους δίνει κατεύθυνση και ότι αν θεωρούμε πως πρέπει να γνωρίζει την αιτιολόγηση της κάθε ψήφου τους «είμαστε γελασμένοι». Μόνο που αυτό είναι κάπως αστείο. 📌 Μιλάμε για όλους τους ευρωβουλευτές του κυβερνώντος κόμματος, οι οποίοι ψηφίζουν συντονισμένα πάνω σε ένα θέμα που αφορά άμεσα τις σχέσεις της Ελλάδας με ένα άλλο κράτος. Και καλούμαστε στα σοβαρά να πιστέψουμε ότι το έκαναν όλοι από μόνοι τους, χωρίς καμία πολιτική κατεύθυνση ή συνεννόηση, και ότι η κυβέρνηση δεν γνωρίζει καν γιατί. Και υπάρχει και κάτι ακόμα. Όταν τη συμφέρει πολιτικά, η κυβέρνηση μια χαρά σχολιάζει τις ψήφους στο Ευρωπαϊκό Κοινοβούλιο. Στις 18 Ιουνίου, ο ίδιος ο κυβερνητικός εκπρόσωπος σχολίασε από αυτό το βήμα πώς ψήφισαν Έλληνες ευρωβουλευτές και δήλωσε ότι «έπεσαν οι μάσκες» για τη στάση της αντιπολίτευσης. Στις 12 Φεβρουαρίου, πάλι για ψηφοφορία στο Ευρωπαϊκό Κοινοβούλιο, έλεγε ότι «η στάση των ευρωβουλευτών της Νέας Δημοκρατίας ήταν ξεκάθαρη». Οπότε επιστρέψαμε στην επόμενη ενημέρωση και θέσαμε ξανά το ερώτημα. Τώρα πια ο κυβερνητικός εκπρόσωπος είχε ζητήσει, όπως είχε υποσχεθεί, ενημέρωση από την ευρωομάδα της Νέας Δημοκρατίας. Άρα περιμέναμε επιτέλους να μάθουμε: Γιατί ψήφισαν «όχι»; Και τότε έγινε πολύ πιο εμφανές γιατί την πρώτη φορά δεν υπήρχε απάντηση. Η απάντηση που πήραμε μετά την ενημέρωση ήταν ουσιαστικά μηδέν: 👉 Οι ευρωβουλευτές της ΝΔ ακολούθησαν τη στάση του Ευρωπαϊκού Λαϊκού Κόμματος και των Σοσιαλιστών απέναντι σε μια τροπολογία της Ευρωπαϊκής Αριστεράς. Δηλαδή: «Το κάναμε γιατί το έκαναν και οι άλλοι». Τίποτα επί της ουσίας. ❓ Γιατί διαφωνούσαν με την τροπολογία; ❓ Γιατί ψήφισαν κατά της καταδίκης τέτοιων παρεμβάσεων; ❓ Τι ακριβώς θεωρούσαν λανθασμένο; Καμία απάντηση. Γι’ αυτό το θέσαμε όσο πιο απλά γινόταν: Αν οι τουρκικές Αρχές επενέβαιναν σε μια εκλογική διαδικασία στην Ελλάδα, προφανώς θα το καταδίκαζαν. Με το #Ισραήλ τι συμβαίνει; Άλλο κράτος είναι κι αυτό. Με άλλα συμφέροντα... #Δημοκρατία #Ευρώπη #Πολιτική

11584
newsORF.at 3w

Die OpenAI-KI hat 53 Nutzerbilder ohne öffentliche Links auf Onlineplattformen veröffentlicht und war zudem auf US-Regierungswebsites aktiv, wo sie auf öffentliche Informationen zugriff, während weitere Enthüllungen über eigenständige Hackingaktivitäten zu erwarten sind. #OpenAI #KünstlicheIntelligenz #Datenschutz

orf.at
OpenAI-KI veröffentlichte Nutzerbilder auf Plattformen
1738
Anthony Albanese 3w

Ova objava dolazi samo nekoliko dana nakon što je australski premijer Anthony Albanese izvijestio da su OpenAI-jevi agenti pristupili privatnim datotekama Medicare-a, australskog državnog zdravstvenog sustava. #AI #sigurnost #hacking

OpenAI priznao da su njegovi AI agenti hakirali vladine stranice
www.index.hr
2201