WRLD

Search

#Informatique
La Libre.be 1d

Zuhal Demir, the current Flemish Minister of Education, questions the necessity of laptops in schools and has canceled the plan to provide each student with a computer, with schools now only required to provide access to IT facilities. #Éducation #Informatique #Flandre (translated)
www.lalibre.be
Si cela ne tenait qu’à Zuhal Demir, il n’y aurait plus d’ordinateurs dans les écoles flamandes
2484
Team Vitality 🐝 2d

Team Vitality indicated that the club's premises had been looted during the mobilization on October 17. The club specified that no staff members or fans had been injured, but that its display cases had been destroyed and trophies as well as computer equipment had been stolen. Pending a full assessment of the damage, V.Hive would remain closed, Team Vitality added, announcing that further information would be communicated later. #Justice #Solidarité #Soutien (translated)

2870
BFMTV 3d

The General Conference on Weights and Measures has decided to abolish the leap second starting in 2027 to avoid major computer issues related to time synchronization. #temps #seconde #scientifiques (translated)

www.bfmtv.com
Terminé 23h59:60 sur vos horloges, les scientifiques veulent supprimer la seconde "intercalaire"
3131
SaxX ¯\_(ツ)_/¯ 3d

SaxX reported that a hacker had accessed the Danish central registry of persons, the CPR, and retrieved data associated with about 8.8 million identification numbers. According to him, these concerned living people, deceased individuals, or those who had gone abroad, and included names, addresses, and personal numbers. The author clarified that the intrusion did not directly target the Danish state, but Pays ApS, an IT company in Odense that had legal access to the registry to verify its clients' files. He indicated that the company had only two employees. Citing the newspaper Politiken, he wrote that at least three of its accounts used the password "123456", including that of the administrator. According to SaxX's account, the hacker allegedly used a leaked password from a former employee, maintained access for 21 days and 17 hours, and carried out about 14 million automated searches between September 10 and 20. The hacker also claimed that his data recovery program had been written by an AI, that he had no particular technical skills, and that he did not intend to sell or publish the data. SaxX stated that the intrusion was only discovered on October 2, after an official noticed an abnormally high bill, as searches in the registry are paid. He added that the Minister of Digital Affairs had described the incident as "deeply serious." The author also reported that the number of citizens who activated a credit fraud alert had risen from about 250,000 to nearly 970,000 in one week. According to him, the CPR had then reminded the security rules to 1,039 companies that had access to the registry, including banks, telecom operators, law firms, unions, and insurers. Finally, SaxX estimated that the incident demonstrated the risks associated with access granted to private providers, as several African states digitized their civil registries. #Cybersécurité #Hacking #Danemark (translated)

3474
Les Mileistes Français 🦁🇫🇷 3d

French Mileists claimed that Americans had just invented a flying car and presented this advancement as one of the American innovations that have transformed the world in the last twenty years. They cited AI, smartphones, film photography, cloud computing, mass-produced autonomous and electric cars, reusable rockets, streaming, and social networks. They also mentioned quantum computing, next-generation supersonic planes, and mini nuclear power plants as upcoming innovations. The account estimated that European intellectuals would probably downplay this advancement and called on Europe to reconnect with the ambition of conquest and change. It judged that the continent had mentally remained in 1998 and was no longer participating, in its opinion, in writing the future. https://t.co/70LUch3w0I #Innovation #Technologie #Futur (translated)

3362
Franceinfo 4d

The General Secretariat for Defense and National Security was subjected to a cyber attack this Tuesday, with no data leakage reported according to its officials. #cybersécurité #attaqueinformatique #SGDSN (translated)

www.franceinfo.fr
Le secrétariat général de la défense et de la sécurité nationale a été la cible d’une attaque informatique ce mardi, aucune fuite de données constatée
2696
Damien Rieu 4d

The author stated that the French colonial empire had been an economic burden, contrary to a widespread belief. According to him, its abandonment had allowed for the reorientation of investments towards technological innovation, particularly the TGV, nuclear energy, the Concorde, space exploration, and computer science. (translated)

2925
Le Parisien 5d

A widespread computer bug in 2035 could be avoided thanks to a diplomatic battle, despite the obstacles posed by Russia. #buginformatique #bataillediplomatique #scenariodystopique (translated)

www.leparisien.fr
Un bug informatique généralisé en 2035 ? La bataille diplomatique pour éviter ce scénario, malgré des freins de la Russie
2819
BFMTV 5d

Alessandro Curioni, vice president of IBM Europe and Africa, warns about the risks of massive hacking related to quantum computing, emphasizing that less than 10% of organizations are currently resistant to this technology capable of compromising essential encryption systems for financial and personal security. #Cybersécurité #InformatiqueQuantique #IBM (translated)

www.bfmtv.com
Des institutions financières au contrat de votre maison: un dirigeant d'IBM alerte sur le risque de piratages massifs lié à l'informatique quantique
2932
Cerfia 5d

Cerfia, citing French breaches, listed the administrations, state services, and French public operators that may have been targeted by cyberattacks or data leaks over the past year. In the employment and social benefits sector, Cerfia reported data concerning up to 12 million employees in the URSSAF/DPAE system: names, dates of birth, employers, and hire dates. For URSSAF/Pajemploi, the figure was 1.2 million employees, with identities, addresses, social security numbers, and bank names. The census also mentioned 1.6 million young people linked to France Travail and local missions, whose identities, addresses, phone numbers, and social security numbers may have been affected. For Pass'Sport and the Ministry of Sports, it mentioned 3.5 million households along with their names, contact details, phone numbers, and addresses. It also reported nearly 1.2 million CAF/CNAF/Vacaf files claimed, without confirmation from CNAF, regarding family information, beneficiaries, and vacation stays. Cerfia also reported that Bloctel/DGCCRF had about 3 million phone numbers extracted, including 600,000 registered on Bloctel. The Agency for Services and Payment and the Coup de pouce énergie scheme may have involved 108,555 beneficiaries, with their identities, addresses, amounts of assistance, and IBANs. A link mentioned in the post referred to a service that may have affected 550,000 accounts, with names, emails, phones, dates of birth, and engagement histories. France Travail may also have been affected by agent data held by an HR service provider, while France VAE may have seen candidate data targeted. In education and training, the census reported 5.8 million DELF-DALF candidates associated with France Éducation International and GAEL, whose identities, nationalities, dates, and places of birth may have been exposed. For the Ministry of National Education, it mentioned up to 4.35 million teachers potentially affected by identity, assignment, grade, and compensation data, as well as one million students from Créteil whose personal and family data may have been exfiltrated. The COMPAS system may have involved 243,000 agents, with their names, personal addresses, and initial assignments. Up to 200,000 candidates for Ev@lang may have been affected by personal data related to language tests. Cerfia also cited ÉduConnect. The post mentioned 705,000 Parcoursup candidates in the academic region of Occitanie, whose identities, contact details, school information, scholarship status, and family data may have been affected. The intrusion was dated to October 2025. For the Ministry of Sports and FORÔMES, it advanced 450,000 candidates and identity, address, phone number, date of birth, and diploma level data. The Compte Asso was also among the mentioned services. Cerfia further reported at least 30 affected sports federations — notably in football, shooting, tennis, gymnastics, swimming, sailing, skiing, and handball — with data from license holders, including minors. At least eight public higher education institutions were cited: Angers, Lille, UMLP, Alfort, Bordeaux Sciences Agro, AgroParisTech, CNAM, and ésam. The post also mentioned the training platform of the Agency for Civic Service and the application platforms of Campus France. Among financial and administrative organizations, Cerfia reported that about 1.2 million bank accounts linked to DGFiP/FICOBA may have been affected, with identities, addresses, RIBs, and IBANs. Up to 433,485 individuals may have been impacted through the DGFiP property register, with addresses and characteristics of real estate. More than 350,000 individuals may have been affected by tax data — reference tax income, family quotients, and withholding rates — and the portal for vacant inheritances was also listed. For DGAFP/Choosing Public Service, the figure mentioned was 377,418 candidates, with their identities, contact details, diplomas, and professional backgrounds. The post also cited the Ministry of the Interior and the TAJ, FPR, SIA, and SIV files. The census mentioned 774,000 people linked to Cnous/CROUS, with identities, emails, and appointments. It also reported 329,000 extracted documents concerning 139,000 individuals, including identity and income verification documents. ANFR/Radiomaritime may have concerned 330,000 users and their identities, addresses, emails, phones, and dates of birth. For INSEE, Cerfia reported 12,800 agents and former agents, with identities and professional contact details. The Institute for Research and Development may have involved about 7,500 individuals, with identity, address, and professional data along with, for some, social security numbers; exfiltration was not confirmed. The post also cited CNRS and personnel data. Cerfia indicated that Public Health France and a service provider may have been involved for about 80,000 contacts: names, emails, addresses, and professional phones, without any reported medical data. For Tracfin and a support provider, it mentioned 136 professionals, their identities and contact details, as well as 213 assistance requests; according to ANSSI, no suspicion declarations were reported. ANSSI and its innovation laboratory were also listed, with 118 Metabase accounts potentially affected by a compromise. The post further cited 70,000 files and 160,000 administrative documents that may have been exfiltrated from DINUM/HubEE, some containing personal data, as well as the State Cloud. More than 30,000 individuals may have been affected by directory, identity, and professional contact data related to AEFE/Orion. At the Ministry of Ecological Transition, 22,000 agents and accredited organizations may have been involved with access to personal data, and over 300 email accounts may have been compromised. Cerfia also mentioned messaging services and a server from the General Directorate of Customs and Indirect Rights, as well as Tchap, the secure messaging service of the State. Finally, the census reported 14 SDIS targeted, with personal and professional data, internal documents, and medical data. At least five hospital establishments may have been affected: AP-HP, Hospices Civils de Lyon, as well as the establishments in Perpignan, Chaumont, and Haute-Comté. The list also included the French Office for Biodiversity and hunting permits, the National Library of France, and the Center for National Monuments through a ticketing service provider, regional health agencies and vaccination data, as well as the French Office for Immigration and Integration and an IT service provider. #Cyberattaques #ProtectionDesDonnées #SécuritéInformatique (translated)

3615
La Libre.be 5d

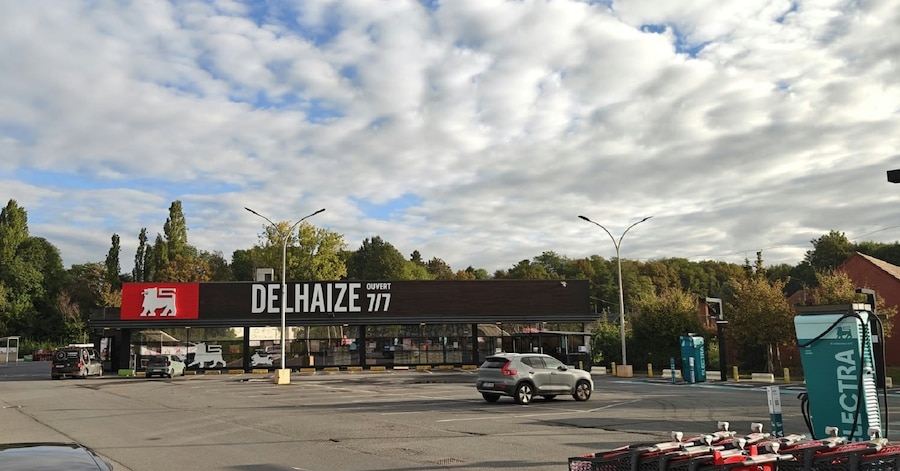
Delhaize has been facing an alternative supply since three days ago due to a computer incident at its parent company Ahold Delhaize, without customers feeling much impact. #Delhaize #cybersécurité #approvisionnement (translated)

www.lalibre.be
Delhaize contraint à un approvisionnement alternatif après un incident informatique
2711
Franceinfo 5d

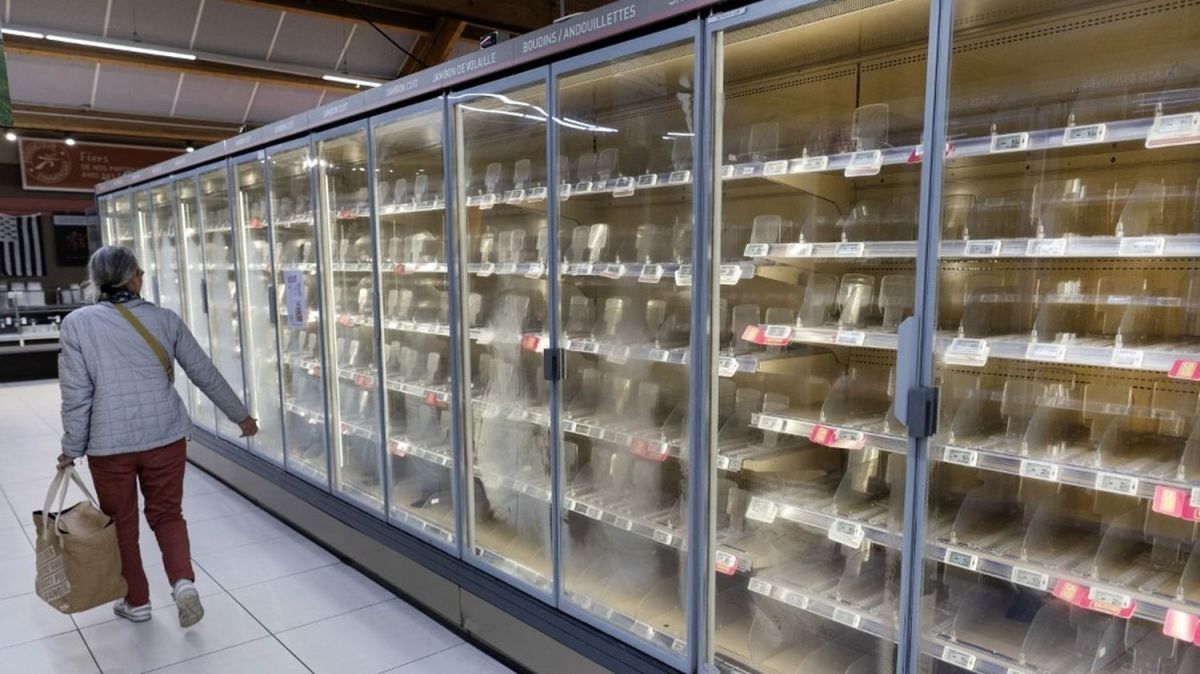
A recent cyberattack disrupted the refrigeration systems of hundreds of supermarkets in France, highlighting the vulnerability of connected devices to cyber threats and the lack of security often observed in their design. #cybersécurité #objetsconnectés #risquesinformatiques (translated)

www.franceinfo.fr
"Un risque que beaucoup d'entreprises sous-estiment" : pourquoi les frigos de supermarchés et autres objets connectés sont-ils si vulnérables face aux cyberattaques ?
2599
BFMTV 6d

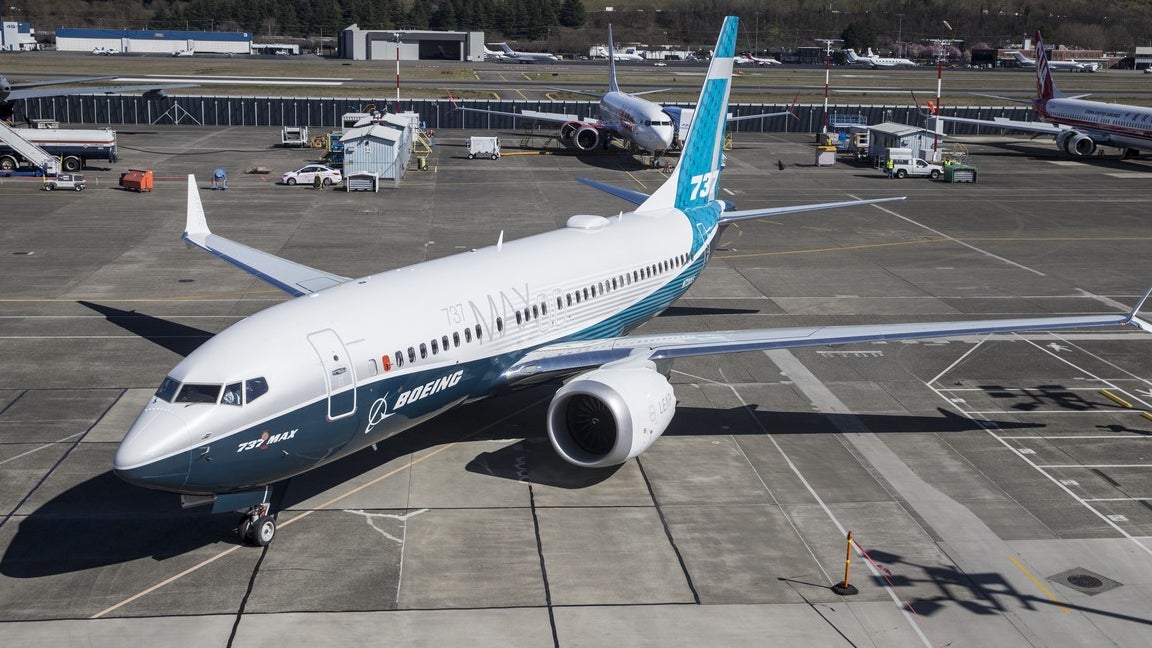
Boeing recorded a record 363 deliveries of its 737 MAX during the first nine months of the year, despite a recent computer bug deemed not concerning by the American regulator. #Boeing #737Max #Aéronautique (translated)

www.bfmtv.com
Boeing n'a jamais livré autant de 737 Max en 9 mois: l'avionneur américain a remis à ses clients 363 exemplaires de sa famille vedette depuis le début de l'année
2829
L
Le Soir 6d

Ahold Delhaize is facing unresolved IT issues affecting its Albert Heijn and Delhaize supermarkets, leading to the downtime of several services and disrupting supply. #AholdDelhaize #cyberattaque #problèmesinformatiques (translated)

www.lesoir.be
Ahold Delhaize toujours confronté à des problèmes informatiques
2833
L
Le Soir 6d

The IT problems affecting the Albert Heijn and Delhaize supermarket chains in Belgium, related to a cybersecurity incident, have still not been resolved despite Ahold Delhaize's efforts to address the situation. #Delhaize #Cyberattaque #ProblèmesInformatiques (translated)

www.lesoir.be
Les problèmes informatiques qui touchent Delhaize toujours pas résolus : ce que cela implique
2720
Zuhal Demir 6d

The entities thus have distinct support services for staff, accounting, and IT. According to Zuhal Demir, this distribution is outdated and inefficient. #Enseignement #Réforme #Flandre (translated)

Un nouveau « ministère de l’Enseignement » : une grande réforme envisagée en Flandre
www.lesoir.be
2947
Nicolas Henin 7d

- Be careful with your computer security and especially keep your software up to date. - Meh. It's okay... I don't work in a high-risk sector. - Oh yes, what do you do? - I manage supermarket freezers... (translated)

2612
L
Le Soir 7d

Delhaize is facing a computer incident that does not affect the opening of its stores in Belgium and Luxembourg, but temporarily makes its customer service unreachable. #Delhaize #IncidentInformatique #Clients (translated)

www.lesoir.be
Delhaize confrontée à un incident informatique : quel impact pour ses clients en Belgique ?
2726
Louis Duclos 7d

Louis Duclos wrote that a large-scale cyberattack struck several major French retailers on Monday. According to him, nearly 150 Intermarché stores would have been affected, with losses potentially reaching several million euros nationwide. He stated that hackers had gained remote control of refrigeration regulation systems manufactured by Danfoss, causing forced and continuous defrosting with programmed temperatures of up to 50 °C. Duclos added that stocks of fresh and frozen products were destroyed within hours and that two supermarkets in Haguenau were already reporting 270,000 euros worth of lost goods. He also highlighted the associated food waste. Duclos estimated that the attack revealed a worrying vulnerability for national security. In the event of a conflict, he wrote, a hostile power could exploit such a flaw to simultaneously disrupt thousands of refrigeration facilities, destroy food stocks, and disrupt supply chains in France. He argued that the digital dependence of the food supply chain constituted a potential destabilization leverage and that this threat must be taken very seriously. #Cyberattaque #Sécurité #Alimentation (translated)

3634
Jon De Lorraine 7d

Jon De Lorraine stated that a cyberattack targeted the refrigerated facilities of several French brands, including Intermarché, Leclerc, and Super U. According to his message, the hackers exploited control systems from the manufacturer Danfoss and hijacked the defrost function, causing continuous operation and set temperatures reaching 50 °C. He indicated that around 150 Intermarché stores would be affected and that stock of fresh and frozen products would have been destroyed. In Haguenau, in Alsace, two supermarkets reportedly suffered losses of 270,000 euros, he wrote, adding that the national toll could reach several million euros. He cited BFM and Je Bosse en Grande Distribution as sources and specified that the assessments were still provisional. #Cyberattaque #SécuritéInformatique #Supermarchés (translated)

3521