Supermarkets are facing empty shelves due to unclaimed cyberattacks, forcing a disruption of supply chains and a return to traditional methods until the situation is resolved. #cyberattaques #supermarchés #crise (translated)
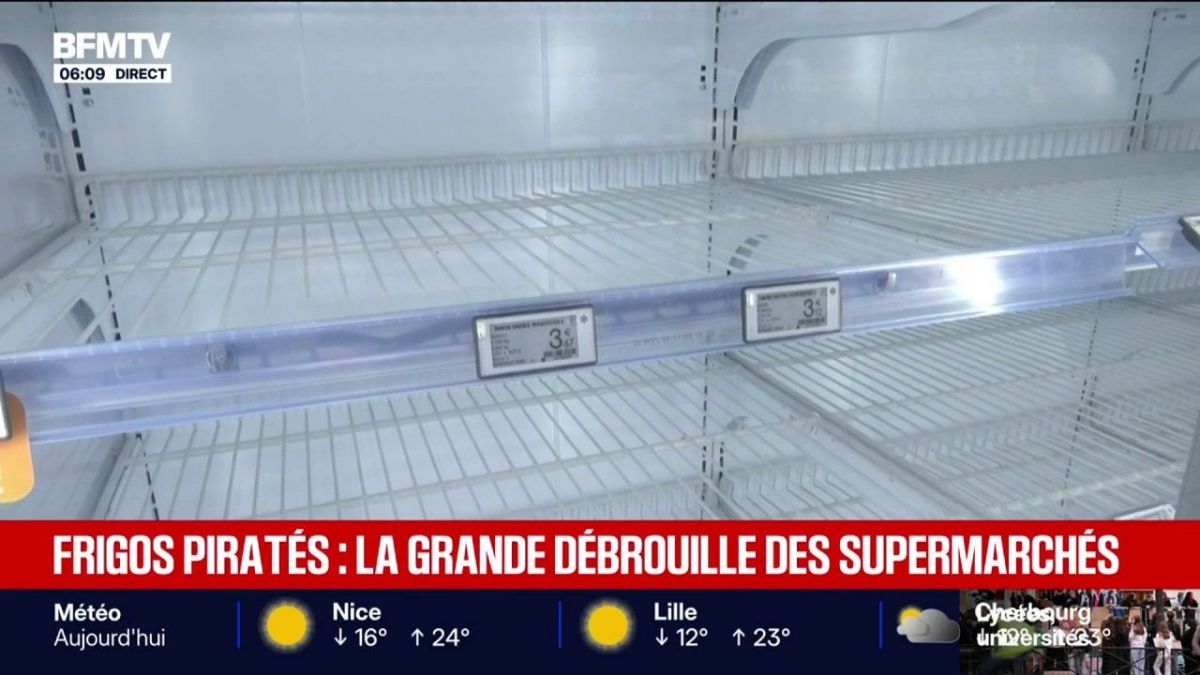
Supermarkets are facing empty shelves due to unclaimed cyberattacks, forcing a disruption of supply chains and a return to traditional methods until the situation is resolved. #cyberattaques #supermarchés #crise (translated)

Since the beginning of Russia's invasion of Ukraine in February 2022, European countries have faced an escalation of hostile Russian actions, ranging from cyberattacks to maritime incidents, aimed at undermining their infrastructures and destabilizing their democratic societies. #GuerreEnUkraine #Cyberattaque #InvasionRussie (translated)

Cerfia, citing French breaches, listed the administrations, state services, and French public operators that may have been targeted by cyberattacks or data leaks over the past year. In the employment and social benefits sector, Cerfia reported data concerning up to 12 million employees in the URSSAF/DPAE system: names, dates of birth, employers, and hire dates. For URSSAF/Pajemploi, the figure was 1.2 million employees, with identities, addresses, social security numbers, and bank names. The census also mentioned 1.6 million young people linked to France Travail and local missions, whose identities, addresses, phone numbers, and social security numbers may have been affected. For Pass'Sport and the Ministry of Sports, it mentioned 3.5 million households along with their names, contact details, phone numbers, and addresses. It also reported nearly 1.2 million CAF/CNAF/Vacaf files claimed, without confirmation from CNAF, regarding family information, beneficiaries, and vacation stays. Cerfia also reported that Bloctel/DGCCRF had about 3 million phone numbers extracted, including 600,000 registered on Bloctel. The Agency for Services and Payment and the Coup de pouce énergie scheme may have involved 108,555 beneficiaries, with their identities, addresses, amounts of assistance, and IBANs. A link mentioned in the post referred to a service that may have affected 550,000 accounts, with names, emails, phones, dates of birth, and engagement histories. France Travail may also have been affected by agent data held by an HR service provider, while France VAE may have seen candidate data targeted. In education and training, the census reported 5.8 million DELF-DALF candidates associated with France Éducation International and GAEL, whose identities, nationalities, dates, and places of birth may have been exposed. For the Ministry of National Education, it mentioned up to 4.35 million teachers potentially affected by identity, assignment, grade, and compensation data, as well as one million students from Créteil whose personal and family data may have been exfiltrated. The COMPAS system may have involved 243,000 agents, with their names, personal addresses, and initial assignments. Up to 200,000 candidates for Ev@lang may have been affected by personal data related to language tests. Cerfia also cited ÉduConnect. The post mentioned 705,000 Parcoursup candidates in the academic region of Occitanie, whose identities, contact details, school information, scholarship status, and family data may have been affected. The intrusion was dated to October 2025. For the Ministry of Sports and FORÔMES, it advanced 450,000 candidates and identity, address, phone number, date of birth, and diploma level data. The Compte Asso was also among the mentioned services. Cerfia further reported at least 30 affected sports federations — notably in football, shooting, tennis, gymnastics, swimming, sailing, skiing, and handball — with data from license holders, including minors. At least eight public higher education institutions were cited: Angers, Lille, UMLP, Alfort, Bordeaux Sciences Agro, AgroParisTech, CNAM, and ésam. The post also mentioned the training platform of the Agency for Civic Service and the application platforms of Campus France. Among financial and administrative organizations, Cerfia reported that about 1.2 million bank accounts linked to DGFiP/FICOBA may have been affected, with identities, addresses, RIBs, and IBANs. Up to 433,485 individuals may have been impacted through the DGFiP property register, with addresses and characteristics of real estate. More than 350,000 individuals may have been affected by tax data — reference tax income, family quotients, and withholding rates — and the portal for vacant inheritances was also listed. For DGAFP/Choosing Public Service, the figure mentioned was 377,418 candidates, with their identities, contact details, diplomas, and professional backgrounds. The post also cited the Ministry of the Interior and the TAJ, FPR, SIA, and SIV files. The census mentioned 774,000 people linked to Cnous/CROUS, with identities, emails, and appointments. It also reported 329,000 extracted documents concerning 139,000 individuals, including identity and income verification documents. ANFR/Radiomaritime may have concerned 330,000 users and their identities, addresses, emails, phones, and dates of birth. For INSEE, Cerfia reported 12,800 agents and former agents, with identities and professional contact details. The Institute for Research and Development may have involved about 7,500 individuals, with identity, address, and professional data along with, for some, social security numbers; exfiltration was not confirmed. The post also cited CNRS and personnel data. Cerfia indicated that Public Health France and a service provider may have been involved for about 80,000 contacts: names, emails, addresses, and professional phones, without any reported medical data. For Tracfin and a support provider, it mentioned 136 professionals, their identities and contact details, as well as 213 assistance requests; according to ANSSI, no suspicion declarations were reported. ANSSI and its innovation laboratory were also listed, with 118 Metabase accounts potentially affected by a compromise. The post further cited 70,000 files and 160,000 administrative documents that may have been exfiltrated from DINUM/HubEE, some containing personal data, as well as the State Cloud. More than 30,000 individuals may have been affected by directory, identity, and professional contact data related to AEFE/Orion. At the Ministry of Ecological Transition, 22,000 agents and accredited organizations may have been involved with access to personal data, and over 300 email accounts may have been compromised. Cerfia also mentioned messaging services and a server from the General Directorate of Customs and Indirect Rights, as well as Tchap, the secure messaging service of the State. Finally, the census reported 14 SDIS targeted, with personal and professional data, internal documents, and medical data. At least five hospital establishments may have been affected: AP-HP, Hospices Civils de Lyon, as well as the establishments in Perpignan, Chaumont, and Haute-Comté. The list also included the French Office for Biodiversity and hunting permits, the National Library of France, and the Center for National Monuments through a ticketing service provider, regional health agencies and vaccination data, as well as the French Office for Immigration and Integration and an IT service provider. #Cyberattaques #ProtectionDesDonnées #SécuritéInformatique (translated)
SaxX stated that hundreds of French supermarkets had seen their freezers reach 50 °C on Sunday evening, in what he described as a cyberattack that led to the destruction of frozen goods and estimated losses of several million euros. However, he clarified that the vector of the attack had not been confirmed and that no group had claimed responsibility. According to SaxX, the AK-SM controllers from Danfoss, which manage refrigeration in stores, were accessible from the Internet. He recalled that Danfoss had declared the AK-SM 800 model end-of-life in 2021, and that 16 Russian supermarkets equipped with these devices had been attacked in 2022. In 2023, Synacktiv reported an authentication bypass, to which the manufacturer allegedly responded that the issue concerned end-of-life products. In 2025, Claroty discovered a password calculated from the current date. SaxX added that Claroty had presented its work at the DEFCON conference in Las Vegas in August 2026, demonstrating how this vulnerability could be exploited to cut refrigeration and display false temperatures. He mentioned more than 2,700 exposed controllers worldwide and indicated that Danfoss had acknowledged that most of the affected equipment was old and unpatched. He also cited Dixell as another impacted manufacturer. The author estimated that France accounted for nearly 60% of the exposed Danfoss controllers reported worldwide, according to Internet scans he claimed to have consulted. He also mentioned the presence of these devices in South Africa and the risk that African supermarkets could be affected, particularly due to the use of refurbished equipment. Finally, SaxX condemned a lack of accountability, writing that researchers had alerted to the vulnerabilities while stores had continued to use the equipment. #cybersécurité #cyberattaque #supermarchés (translated)
The article examines the growing vulnerability of essential infrastructures, such as supermarkets and transportation systems, to cyberattacks, highlighting the implications for data security and connected assets. #Cyberattaques #SécuritéInformatique #Vulnerabilités (translated)
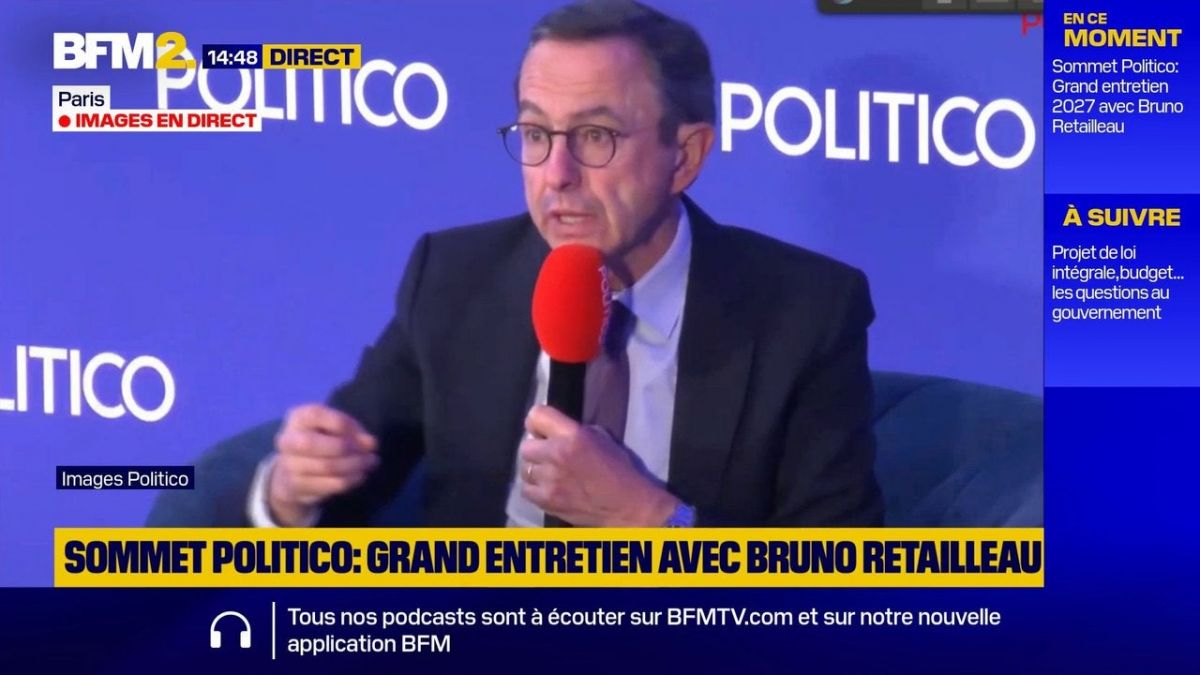
Our companies are very poorly protected. In the face of cyberattacks, "our companies are very poorly protected," denounces Bruno Retailleau. #MobilisationLycéenne #Macron #NPAJeunes (translated)
Our businesses are very poorly protected. In the face of cyberattacks, "our businesses are very poorly protected," denounces Bruno Retailleau. #Cyberattaques #SécuritéInformatique #BrunoRetailleau (translated)
Bruno Retailleau expressed his concerns about the insufficient protection of French companies against cyberattacks during the Politico summit on economic competitiveness. #Cyberattaques #SécuritéInformatique #BrunoRetailleau (translated)

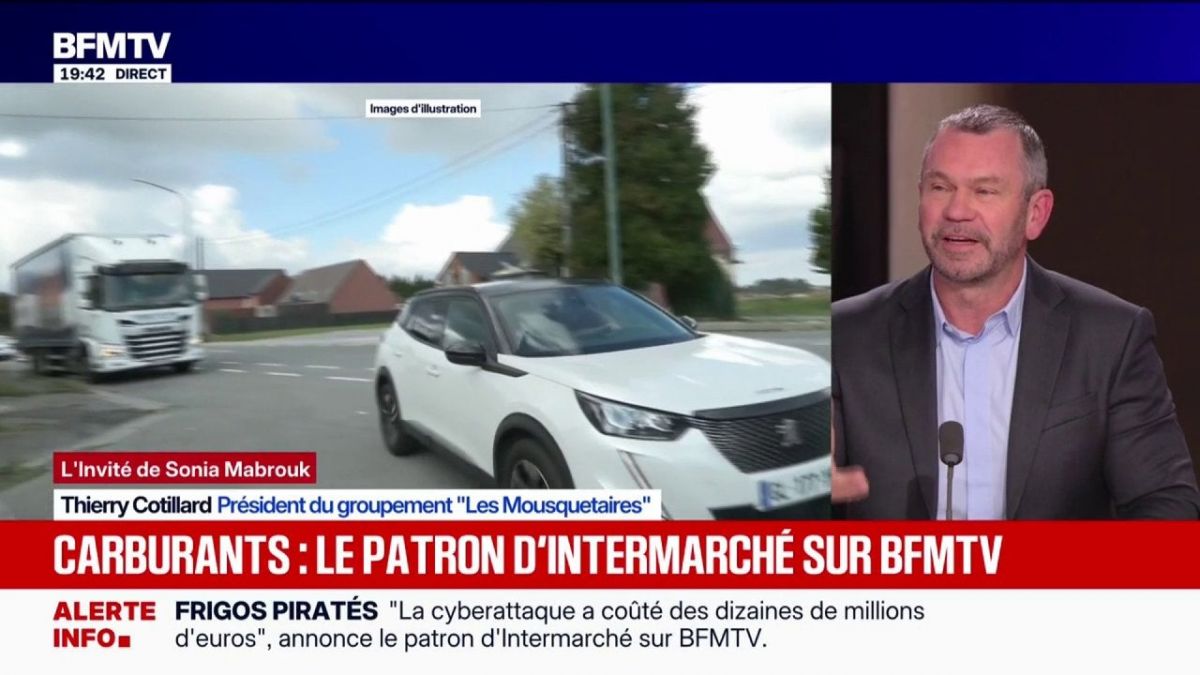
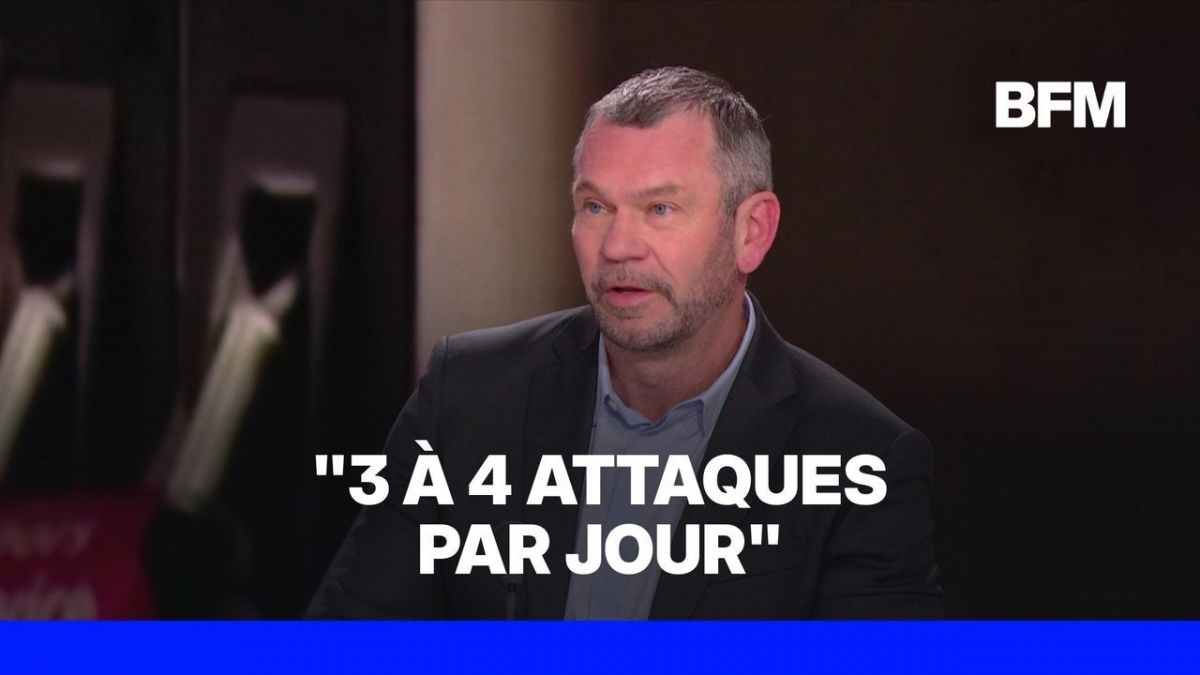
Thierry Cotillard, CEO of Intermarché, stated that the recent cyberattack affecting 300 stores of his brand and less than a hundred U stores, by remotely altering the temperatures of refrigeration systems, is just one example among 3 to 4 cyberattacks per day that they face. #cyberattaque #Intermarché #sécuritéinformatique (translated)

Thierry Cotillard, president of the Les Mousquetaires group, warns about the gravity of cyberattacks, reporting that 300 Intermarché and Netto stores have been affected by an attack targeting refrigeration control systems, leading to significant losses of fresh and frozen product stocks. #cyberattaque #sécuritéinformatique #distribution (translated)

Cyberattack on supermarkets: Thierry Cotillard, president of the group Les Mousquetaires, mentions "3 to 4 cyberattacks per day." #cyberattaque #supermarchés #LesMousquetaires (translated)
Thierry Cotillard, president of the Les Mousquetaires group, stated that French supermarkets are now experiencing 3 to 4 cyberattacks per day, one of which recently exploited a vulnerability in refrigeration systems, resulting in the destruction of stocks of fresh and frozen products. #cyberattaque #supermarchés #LesMousquetaires (translated)

"Cyberattacks will be the most significant challenge in the coming year": Bill Gates is concerned about the destructive potential of AI in cybersecurity, much more immediate than an "uncontrollable AI." #Meta #RGPD #Publicité (translated)
SaxX estimated that France was very vulnerable in terms of cybersecurity and considered the situation to be serious. He wrote that cyberattacks concerned everyone and called for the creation of a Minister of Cybersecurity position. #Cybersécurité #France #Cyberattaques (translated)
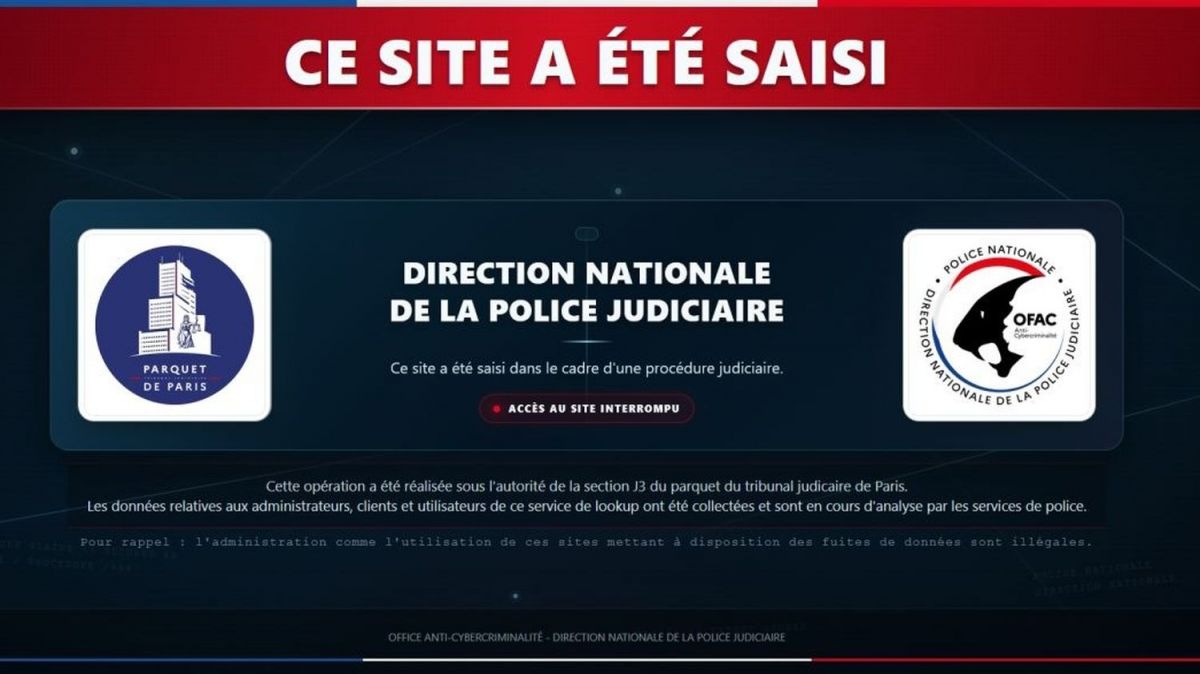
Three 17-year-old teenagers face ten years in prison for operating an illegal search engine, Reacher/Stryxx, which sold stolen personal data during cyberattacks. #cybercriminalité #donnéespersonnelles #lookup (translated)

During an interview, Bill Gates expressed his concerns about the potential rise of cyberattacks fueled by artificial intelligence, viewing them as the main challenge for the upcoming year, ahead of the risk of uncontrollable AI. #Cybersécurité #IntelligenceArtificielle #BillGates (translated)

The developer of the Chinese security tool Artex has decided to close its source code after it was hijacked by malicious actors to carry out cyberattacks, notably in South Korea, resulting in the cessation of updates and technical support. #Cybersécurité #Artex #Piratage (translated)

France is facing a growing vulnerability in cybersecurity, with numerous cyberattacks targeting its businesses and administrations, exacerbated by a lack of resources and the victims' unfamiliarity with the systems. #Cybersécurité #Vulnérabilités #DonnéesPersonnelles (translated)

Despite the increase in cyberattacks and a Senate vote scheduled for early 2025, the review of the resilience law, which aims to strengthen cybersecurity and critical infrastructure in France, is once again delayed in the National Assembly. #Cybersécurité #LoiRésilience #NIS2 (translated)

The company, launched in 2023, particularly highlights its performance in cybersecurity, which is intended to allow "companies and governments to defend themselves against malicious actors" who bypass the protections of closed models to carry out cyberattacks, according to co-founder Guillaume Lample. #IA #Cybersécurité #InnovationFrançaise (translated)