WRLD

Search

#Malware
20 minutos 17h

According to a study by the Graz University of Technology, serious vulnerabilities have been discovered in the data transfer applications of Samsung, Xiaomi, and Google, which could allow cybercriminals close to the device to steal personal information and install malware. #Ciberseguridad #Android #Vulnerabilidades (translated)
www.20minutos.es
Descubren fallos graves en las aplicaciones de Samsung, Xiaomi y Google para pasar los datos de un móvil a otro
2213
Digi24 2d

An Israeli advertising technology company was involved in installing spying software on Al Jazeera devices, infecting 45 computers in the Qatar news network through online ads that contained malware. #Israel #AlJazeera #Spionaj (translated)

www.digi24.ro
O companie israeliană specializată în tehnologia publicitară a contribuit la instalarea de programe spion pe dispozitivele Al Jazeera
2347
20 minutos 2d

The RemControl malware, a banking Trojan for Android that is distributed through fake applications to watch free football, threatens the security of users by stealing banking data and controlling infected devices. #Ciberseguridad #Malware #FútbolGratis (translated)

www.20minutos.es
Buscas una app para ver fútbol gratis y acabas dando acceso a tu banco: así funciona el nuevo malware RemControl
2555
El Español 2d

An Israeli spyware called Candiru has spread through online advertisements, potentially affecting hundreds of millions of users in Spain and in institutions like NATO and the UN, having previously been used in the 'catalangate' against Catalan politicians. #Malware #Ciberseguridad #Espionaje (translated)

www.elespanol.com
Un software espía israelí que ya se usó contra políticos catalanes se propaga mediante anuncios 'online' que alcanzan a España
2701
Barry Malone 2d

The author wrote that Al Jazeera’s finding that 45 of its devices had been compromised prompted a Citizen Lab investigation. The author said the investigation found that an Israeli ad-tech firm had targeted people with malicious ads that were also shown to users on sensitive networks, including the Pentagon, the IAEA and the ICC. #CyberSecurity #Malware #DigitalPrivacy #IL #US

3780
Il Sole 24 ORE 3d

A recent study by Anthropic explores the possibility that artificial intelligence systems could replicate themselves using available computing resources, raising serious questions about cybersecurity and the risk of autonomous malware that could infiltrate devices such as appliances and TVs. #IntelligenzaArtificiale #Cybersicurezza #Malware (translated)

www.ilsole24ore.com
Se l’AI impara a replicarsi: codici malevoli autonomi potrebbero invadere elettrodomestici e Tv
2802
20 minutos 4d

A group of researchers has discovered a malware campaign that affects low-cost Android phones, introducing malicious programs into the firmware before they reach consumers, putting the security of devices at risk in more than 150 countries, including Spain. #Malware #Ciberseguridad #Android (translated)

www.20minutos.es
Estos móviles Android llegan infectados antes de encenderlos: detectan una campaña que también afecta a España
2928
La Libre.be 3w

Un nouveau virus nommé RemControl cible les smartphones Android en Belgique et dans d'autres pays pour voler des informations bancaires, exploitant des fausses publicités et contournant les protections de sécurité. #cybersécurité #malware #Android

www.lalibre.be
Gare à un nouveau virus qui circule sur Android : des utilisateurs touchés en Belgique
1732
Vecernji.hr 3w

Novi bankarski trojanac Gigabud napada aplikacije na Android uređajima, ukrade osjetljive podatke i preuzima kontrolu nad uređajem, a stručnjaci upozoravaju korisnike na rizike povezane s lažnim aplikacijama. #kibernetičkaBezbednost #malware #bankarskiTrojanci

www.vecernji.hr
Novi virus napada bankarske aplikacije na Androidima: Može ukrasti podatke i preuzeti kontrolu nad uređajem
2079
20 minutos 4w

Un nuevo malware llamado KREMLIN se infiltra en los navegadores Chrome y Edge para instalar extensiones maliciosas sin permiso del usuario, robando contraseñas y sesiones a través de documentos falsos disfrazados. #Ciberseguridad #Malware #ExtensionesMaliciosas

www.20minutos.es
Un nuevo malware logra instalar extensiones en Chrome sin permiso para robar contraseñas y sesiones
9874
Magnus Ranstorp Sep 15

UK @NCSC issue warning and advisory: Iranian cyber targeting of dissidents, activists and journalists. Advisory on CHOSEN BRICK malware, including technical analysis and advice to help individuals and organisations protect themselves. #CyberSecurity #Iran #Malware #UK #IR

117
20 minutos Sep 15

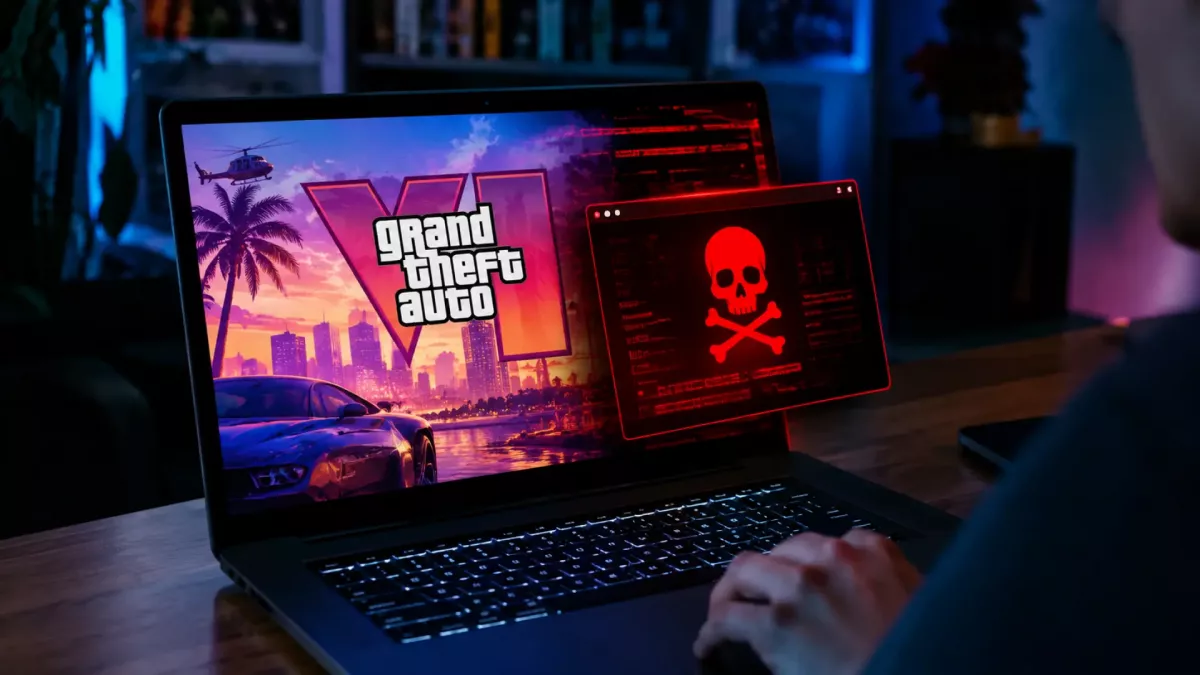
Se advierte a los jugadores que no abran ninguna descarga de GTA 6 antes de su lanzamiento, ya que podría contener malware que amenace la seguridad de sus ordenadores y robe información personal. #GTA6 #Ciberseguridad #Malware

www.20minutos.es
Si encuentras GTA 6 para descargar antes de su lanzamiento, no lo abras
15736
Novinky Sep 14

Článek popisuje, jak ruští hackeři s pomocí umělé inteligence automatizují proces vývoje a úprav malwaru, což značně ztěžuje detekci a obranu proti kybernetickým útokům, přičemž cílem jejich operací byly desítky organizací, včetně vládních úřadů a firem v oblasti obrany. #AI #kybernetickéútoky #malware

www.novinky.cz
Ruští hackeři dovedou snadno přelstít váš antivirus a ani si neušpiní ruce
18081
Ali Utlu Sep 11

Eine neue Android-Schadsoftware namens Mantax Otax verbindet Ransomware mit umfangreichen Spionage- und Fernsteuerungs­funktionen. Die Malware kann Dateien verschlüsseln, Informationen abgreifen und Betroffene gezielt einschüchtern oder belästigen. https://t.co/5RqJ4kvxYr #Malware #Ransomware #CyberSecurity #DE

584
IndexHR Sep 11

Hakeri koriste izvanredno zanimanje za igru GTA 6 kako bi širili opasan malware putem lažnih preuzimanja, ciljajući najnestrpljivije obožavatelje. #GTA6 #sigurnost #malware

www.index.hr
Hakeri koriste hype oko GTA 6 za širenje opasnog malwarea
11098
20 minutos Sep 11

Un malware tipo infostealer está robando las sesiones de usuarios de Claude para consumir sus tokens sin que se den cuenta, lo que ha llevado a Anthropic a emitir una alerta y recomendar medidas de seguridad. #Malware #Claude #Ciberseguridad

www.20minutos.es
¿Usas Claude? Si tus 'tokens' desaparecen solos, puede ser por este malware que los roba
16939
LiveOverflow 🔴 Sep 5

This is an interesting perspective for me. Because my cybersecurity world was "just bugs" long before AI. I think we can trace cyber incidents to one of two root causes: 1. exploited vulnerability (bugs) 2. human error (malware, phishing, ...) In the video, the wider security #Cybersecurity #Vulnerabilities #HumanError #Nospecificcountrycodesarementionedinthetweet.

117
Gianluca Zanella Sep 5

L'ingegner Paolo Reale dimostra (in onda e fuori onda) di interpretare le mie parole a suo piacimento. Prima dice di aver sentito dei video in cui accuso Marco Poggi, Stefania Cappa e compagnia cantante. Poi si mette a ridere quando gli contesto che - se parla di cose che non gli competono - non vado certo a criticarlo come ha fatto lui con me. Ora, ripetiamo tutti insieme: aver scritto decine di articoli sulle intercettazioni telefoniche, non fa di lui - che è un ingegnere informatico - un esperto di intercettazioni telefoniche. Così come io, che ho scritto decine di articoli sul DNA, non sono un esperto di DNA Per fare un esempio calzante, è come se un esperto di intercettazioni telefoniche (uno vero, non Reale) accettasse un incarico da parte di una procura per analizzare un malware informatico. Potrà anche aver scritto decine di articoli. Ma non è un esperto. #Garlasco #Intercettazioni #Expertise #Garlasco

13588
Digi24 Sep 3

România a participat la o operațiune internațională coordonată de FBI pentru destructurarea botnet-ului Sality, o rețea malware activă de peste 20 de ani, implicând distrugerea a peste 11 milioane de adrese IP afectate. #SecuritateCibernetică #BotnetSality #ColaborareInternațională

www.digi24.ro
România, implicată într-o operațiune a FBI împotriva unei rețele cibernetice globale. Milioane de calculatoare, vizate
18166
Novinky Sep 3

Česká společnost ComSource upozornila na nový podvodný trik skupiny WindTapper, která cílí na finanční sektor, využívající kombinaci telefonického vishingu a malwaru WindRelay k získání citlivých údajů a provádění bezkontaktních plateb bez nutnosti fyzického odcizení karty. #vishing #malware #kyberbezpečnost

www.novinky.cz
Kartu nedáte z ruky, přesto s ní podvodník zaplatí. Takto funguje nový trik
10550