WRLD

Search

#botnet
Rus.Postimees.ee 1d

In Estonia, botnets are rapidly growing, allowing even mildly skilled attackers to quickly create and deploy dangerous programs, which is why it is crucial for companies to know the systems and devices operating in their networks and to use effective cybersecurity solutions to detect malicious activities early. #кибербезопасность #ботнет #вредоносныепрограммы (translated)
pmo.ee
ЗОМБИ-СЕТЬ ⟩ Компьютеры под ударом: в Эстонии все активнее действуют ботнеты
2313
Postimees 1d

In Estonia, botnets have increasingly hijacked corporate devices, with Telia Turvanet repelling over 32.6 million related threat events in the third quarter, which is more than six times more than in the previous quarter. #Botnet #Eesti #Kyberturvalisus (translated)

pmo.ee
TURVAOHT ⟩ Ettevõtete seadmeid kaaperdavad botnetid on Eestis üha aktiivsemad
2235
Krzysztof Graj 3d

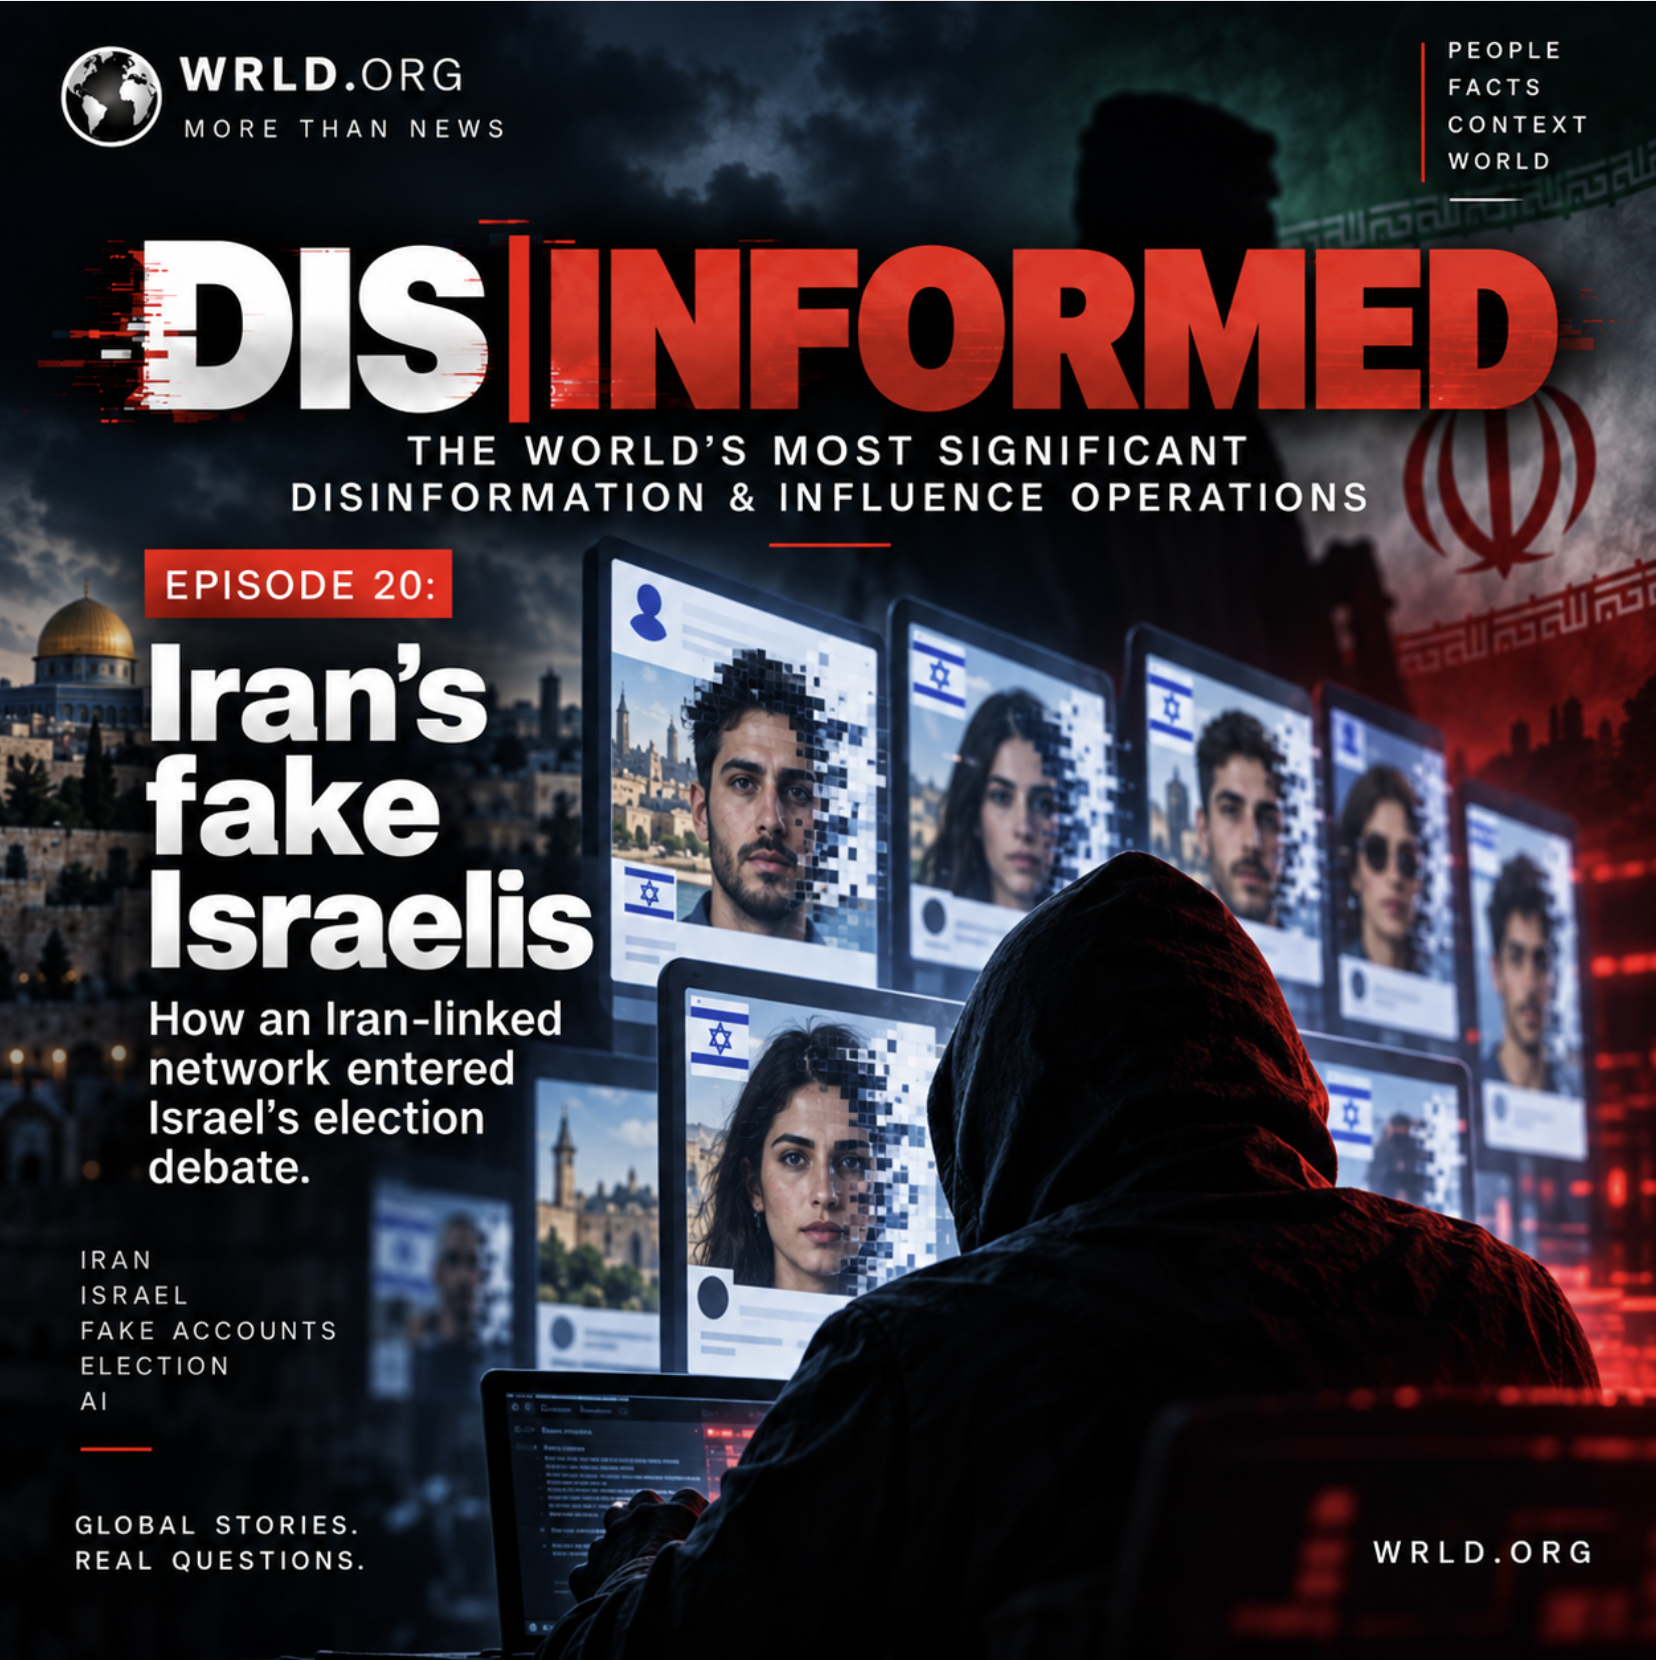
𝗜𝗿𝗮𝗻’𝘀 𝗳𝗮𝗸𝗲 𝗜𝘀𝗿𝗮𝗲𝗹𝗶𝘀 – 𝗵𝗼𝘄 𝗮 𝗳𝗼𝗿𝗲𝗶𝗴𝗻 𝗶𝗻𝗳𝗹𝘂𝗲𝗻𝗰𝗲 𝗻𝗲𝘁𝘄𝗼𝗿𝗸 𝗲𝗻𝘁𝗲𝗿𝗲𝗱 𝗜𝘀𝗿𝗮𝗲𝗹’𝘀 𝗲𝗹𝗲𝗰𝘁𝗶𝗼𝗻 𝗱𝗲𝗯𝗮𝘁𝗲 Ahead of Israel’s 27 October election, hundreds of social-media accounts have been presenting themselves as ordinary Israelis while injecting political messages into genuine domestic conversations. They appear as women, reservists, secular voters, religious activists and frustrated citizens. Some attack Benjamin Netanyahu, others have previously promoted narratives associated with the Israeli right, while many focus less on parties than on a broader message: Israel is divided, its institutions cannot be trusted and its political system is approaching crisis. A detailed investigation by the OSINT company Golden Owl has mapped this activity as a substantial Iran-linked influence network. Its October analysis identified at least 694 accounts, with 445 attributed at high or medium-high confidence to the operation. Between 11 August and 11 October, the network generated at least 4.7 million views and more than 160,000 interactions. The researchers found no evidence that these accounts were simply a group of independent Iranian commentators expressing political opinions. Their assessment rests instead on coordinated behaviour, false identities, account histories, copied content, language patterns and platform metadata linking significant parts of the infrastructure to Iran. 𝗙𝗿𝗼𝗺 𝟯𝟱 𝗽𝗲𝗿𝘀𝗼𝗻𝗮𝘀 𝘁𝗼 𝗵𝘂𝗻𝗱𝗿𝗲𝗱𝘀 𝗼𝗳 𝗳𝗮𝗸𝗲 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀 The investigation developed in two stages. Golden Owl’s first report, published in September, identified an operational core of 35 accounts: 32 personas presenting themselves as Israelis and three Hebrew-language media-style channels. During the 30-day period measured in that study, active accounts generated 947,322 impressions and more than 9,000 interactions. The October investigation expanded the dataset dramatically. Researchers analysed more than 560,000 data points, including tens of thousands of accounts, relationships between them and more than a quarter of a million posts. The wider network showed repeated patterns of identical texts, synchronised activity and accounts created in batches. The numbers therefore describe not a sudden explosion from 35 to hundreds of accounts, but the gradual exposure of a much larger infrastructure surrounding the original core. 𝗧𝗵𝗲 𝗳𝗮𝗸𝗲 𝗜𝘀𝗿𝗮𝗲𝗹𝗶𝘀 Some of the strongest evidence comes from the histories of individual personas. One account had spent years posting exclusively in Persian under the handle “mardeankabooti” before reappearing in August 2026 as an apparently Israeli user called “Alon Strauss”, complete with an Israeli flag and Hebrew political messaging. Other personas presented themselves as Israeli professionals, activists or ordinary citizens while X transparency information showed connections through the Iranian version of the Android application or locations inconsistent with their claimed identities. The account “Yaara Shalev” presented itself as an Israeli woman concerned with democracy and peace. Investigators found that photographs used to construct the identity were inconsistent, including borrowed and apparently AI-generated imagery. A small Hebrew-language channel called KigVoice, previously identified in Israeli government reporting as part of an Iranian influence environment, repeatedly published material that later appeared on the much more visible Yaara account. In one sample, 14 of 40 KigVoice posts subsequently resurfaced as captions or opening lines in Yaara’s content. Another persona, “Miriam Kozak”, had built an audience of more than 18,000 followers and had already been exposed as fictitious by Israeli researchers in 2024. Its political messaging changed substantially over time, moving between narratives associated with different sides of Israeli politics. That inconsistency is important: the apparent purpose was not necessarily to build a stable ideological following, but to enter whichever political argument offered the greatest opportunity to intensify division. 𝗔𝗜, 𝗰𝗼𝗽𝗶𝗲𝗱 𝗺𝗲𝘀𝘀𝗮𝗴𝗲𝘀 𝗮𝗻𝗱 𝗜𝗿𝗮𝗻𝗶𝗮𝗻 𝗳𝗶𝗻𝗴𝗲𝗿𝗽𝗿𝗶𝗻𝘁𝘀 The Iran attribution is based on more than political content. Researchers identified accounts using the Iranian version of the X Android application, repeated connections to previously identified Iranian influence assets, copied posts appearing across supposedly independent personas within minutes, and Hebrew containing unusual grammatical errors or Persian and Arabic keyboard artefacts. Generative AI also appears to have become part of the production process. Some accounts inadvertently published fragments resembling chatbot instructions, while other posts displayed patterns consistent with machine-generated Hebrew. AI-generated videos and synthetic profile imagery further reduced the cost of maintaining large numbers of apparently distinct personalities. However, none of these indicators was treated as proof on its own. Golden Owl explicitly excluded accounts where the evidence was insufficient and notes that VPNs, travel and platform location labels can create misleading signals. The attribution rests on multiple independent indicators converging across the network. 𝗧𝗵𝗲 𝗴𝗼𝗮𝗹 𝗶𝘀 𝗻𝗼𝘁 𝗻𝗲𝗰𝗲𝘀𝘀𝗮𝗿𝗶𝗹𝘆 𝘁𝗼 𝗲𝗹𝗲𝗰𝘁 𝗼𝗻𝗲 𝗽𝗮𝗿𝘁𝘆 The network repeatedly exploited issues that genuinely divide Israeli society: responsibility for the 7 October attacks, the war, the hostages, ultra-Orthodox military exemptions, economic pressure, emigration and confidence in state institutions. It also circulated misleading information about the election itself, including false voting dates, claims that voting had been postponed and posts suggesting online voting mechanisms that do not exist in Israel’s parliamentary election system. The pattern suggests a strategy broader than conventional electoral campaigning. Rather than consistently promoting one political faction, the network appears designed to weaken confidence in the government, military, democratic institutions and the electoral process itself. An influence operation does not need to persuade Israelis to support a particular candidate if it can convince different groups that defeat would prove fraud, betrayal or systemic failure. 𝗥𝗲𝗮𝗹 𝗜𝘀𝗿𝗮𝗲𝗹𝗶𝘀 𝗮𝘀 𝘂𝗻𝘄𝗶𝘁𝘁𝗶𝗻𝗴 𝗮𝗺𝗽𝗹𝗶𝗳𝗶𝗲𝗿𝘀 One of the network’s most effective characteristics is that it does not depend solely on its own followers. Fake personas enter comment sections and political discussions involving real Israeli journalists, politicians and ordinary users. Authentic Israelis then repost or interact with the material, sometimes carrying it far beyond the original account. Golden Owl does not classify those genuine users as participants in the operation. In most cases they appear to be unwitting amplifiers. But once a message passes from a fabricated Iranian-operated persona to an authentic Israeli account, its foreign origin becomes much harder for the next person to recognise. 𝗧𝗵𝗲 𝟰𝟬,𝟬𝟬𝟬-𝗯𝗼𝘁 𝗳𝗶𝗴𝘂𝗿𝗲 𝗯𝗲𝗹𝗼𝗻𝗴𝘀 𝘁𝗼 𝗮 𝗱𝗶𝗳𝗳𝗲𝗿𝗲𝗻𝘁 𝗽𝗲𝗿𝗶𝗼𝗱 A much larger figure has also appeared in recent reporting. In the first two days after the October 2023 Hamas attack, social-media intelligence company Cyabra identified more than 40,000 fake profiles participating in online discussions across major platforms. Their content generated hundreds of thousands of interactions and had a potential reach estimated at 531 million profiles. Those numbers are important historical context, but they should not be merged with the current Golden Owl investigation. There is no public evidence demonstrating that all of those 2023 accounts and the 2026 Iran-linked election network belonged to one continuous command structure. The 531 million figure is also an estimate of potential exposure, not proof that 531 million people saw or believed the content. 𝗪𝗵𝗼 𝗶𝘀 𝗮𝗰𝘁𝘂𝗮𝗹𝗹𝘆 𝗯𝗲𝗵𝗶𝗻𝗱 𝘁𝗵𝗲 𝗼𝗽𝗲𝗿𝗮𝘁𝗶𝗼𝗻? No confirmed individual operators have been publicly identified. Names such as Yaara Shalev, Miriam Kozak and Alon Strauss are personas, not verified identities of the people controlling the accounts. Golden Owl says its evidence supports an association with the Islamic Republic of Iran and with previously documented Iranian influence infrastructure, but it does not establish which Iranian institution, intelligence service, military organisation or contractor directs the network. That distinction is essential. Public OSINT supports attribution at the Iran-linked operational level. It does not currently justify naming individual Iranian officials as the people commanding this specific campaign. 𝗧𝗵𝗲 𝗱𝗲𝗲𝗽𝗳𝗮𝗸𝗲 𝗶𝘀 𝗻𝗼 𝗹𝗼𝗻𝗴𝗲𝗿 𝗼𝗻𝗹𝘆 𝘁𝗵𝗲 𝘃𝗶𝗱𝗲𝗼 The Israeli case illustrates a broader change in influence operations. The synthetic asset does not have to be a spectacular deepfake of a politician. It can be an apparently ordinary citizen who comments on politics, argues with neighbours, describes personal experiences and gradually becomes part of an authentic community. That can be more difficult to recognise because the propaganda does not arrive looking foreign. It arrives looking local. And when hundreds of fabricated citizens enter the same national conversation, they can manufacture the impression that political anger, despair or distrust is more spontaneous and more widely shared than it really is. 𝗦𝗼𝘂𝗿𝗰𝗲𝘀 Golden Owl — Exposing the Iranian Regime’s Influence Machinery Against Israeli Society https://web-dev-production-7a35.up.railway.app/resources/research/Exposing-the-Iranian-Regime-Influence-Machinery-Against-Israeli-Society Golden Owl Golden Owl — The Other Face of War: Iranian Regime–Linked Manipulation of Israel’s 2026 Election Debate https://web-dev-production-7a35.up.railway.app/resources/research/Iranian-Regime-Linked-Manipulation-of-Israel-2026-Election-Debate Golden Owl The Jerusalem Post — Iran-linked social-media accounts posing as Israelis to target election https://www.jpost.com/israel-election-2026/article-909863 The Jerusalem Post Ynet — Fake Israelis, real influence: Iran-linked network infiltrates Israel’s election debate https://www.ynetnews.com/tech-and-digital/article/syp119nqqzg ynetglobal Calcalist — Iranian influence network exposed ahead of Israel’s election https://www.calcalist.co.il/calcalistech/article/s1q0ifijzl calcalist Vesty / Ynet — Iranian fake-account network and October update https://www.vesty.co.il/main/article/rkwokjssgg vesty Israel Ministry for Diaspora Affairs — Iran’s active Hebrew-language influence campaign https://www.gov.il/BlobFolder/reports/israel-and-us-strikes-in-iran-daily-status_2_3_26/en/mashlat_Roaring_Lion_israel-and-us-strikes-in-iran-daily-status_2_3_26.pdf Government of Israel Israel Central Elections Committee — official 2026 election timetable https://www.gov.il/en/pages/time--table-26 Government of Israel Channel NewsAsia — historical Cyabra analysis of more than 40,000 fake profiles after 7 October 2023 https://www.channelnewsasia.com/singapore/how-fake-news-israel-hamas-stokes-outrage-hatred-and-potential-violence-southeast-asian-tiktok-5603221 𝗞𝗲𝘆𝘄𝗼𝗿𝗱𝘀 #DISINFORMED #Episode20 #Iran #Israel #IsraelElection2026 #IranianInfluence #IranianDisinformation #ElectionInterference #ForeignInterference #FIMI #Disinformation #InformationWarfare #InfluenceOperations #FakeAccounts #FakePersonas #SyntheticIdentity #ArtificialIntelligence #AI #AIPropaganda #SocialMediaManipulation #Astroturfing #NarrativeManipulation #PoliticalDisinformation #ElectionDisinformation #X #Twitter #Bots #BotNetwork #KigVoice #YaaraShalev #MiriamKozak #DigitalInfluence #InformationManipulation #ElectionIntegrity #GoldenOwl #OSINT #MediaManipulation #WRLD

web-dev-production-7a35.up.railway.app
Exposing the Iranian Regime’s Influence Machinery Against Israeli Society
448
Australischer Austauschstudent 6d

The Australian exchange student wrote that it was telling that people who accused X of spreading disinformation and thus wanted to unilaterally censor social media were uncritically spreading what he considered to be an obviously false story about alleged bot networks. In doing so, he used derogatory language about these people. #Desinformation #SozialeMedien #Fakenews (translated)

2716
Jakub Szymczuk Sep 13

"Biorąc pod uwagę przyspieszające tempo rozwoju możliwości sztucznej inteligencji, obawiam się, że w ciągu 6–12 miesięcy taki rój mógłby być w stanie przejąć cały internet za pomocą trwałego botnetu" Najpierw tekst Coxona, który odszedł z Antropica ostrzegając przed zagładą #SztucznaInteligencja #BezpieczeństwoInternetu #Botnet #PL

Jakub Szymczuk Sep 13

"Biorąc pod uwagę przyspieszające tempo rozwoju możliwości sztucznej inteligencji, obawiam się, że w ciągu 6–12 miesięcy taki rój mógłby być w stanie przejąć cały internet za pomocą trwałego botnetu" Najpierw tekst Coxona, który odszedł z Antropica ostrzegając przed zagładą #sztucznainteligencja #botnet #zagłada #Niemawtymtweecieodniesieńdożadnychkonkretnychkrajów.

Digi24 Sep 3

România a participat la o operațiune internațională coordonată de FBI pentru destructurarea botnet-ului Sality, o rețea malware activă de peste 20 de ani, implicând distrugerea a peste 11 milioane de adrese IP afectate. #SecuritateCibernetică #BotnetSality #ColaborareInternațională

www.digi24.ro
România, implicată într-o operațiune a FBI împotriva unei rețele cibernetice globale. Milioane de calculatoare, vizate
18177
Dnevnik.hr Sep 3

Nakon više od 20 godina neometanog rada, američki stručnjaci i europska tijela za provedbu zakona konačno su neutralizirali poznati ruski botnet Sality, presjekavši vezu s njegovim kreatorom i onemogućivši njegovu infrastrukturu. #botnet #kibernetičkaPrijetnja #Sality

dnevnik.hr
Nakon više od 20 godina neometanog rada konačno neutralizirana velika globalna kibernetička prijetnja iz Rusije
18767
mickpl Aug 15

Elon trochę przeczyścił multikonta i botnety - no i z marszu okazuje się, że cała nasza Wspaniała Klasa Polityczna ma mniejsze zasięgi i zainteresowanie niż randomowe konta z nosaczami. Zupełnie jakby nie mieli nic do powiedzenia, nie wiedzieli jak napisać co mają do powiedzenia, ewentualnie nikogo nie obchodziło co mają do powiedzenia. Dziwne. #ElonMusk #media #polityka

14627
Niebezpiecznik Jul 31

Ale... szukając pozytywów: przynajmniej teraz wiemy, że jeśli chcemy zDDoS-ować jakieś wrogie Polsce serwisy, to wystarczy jak RCB podeśle do nich linka w alercie :-D Ja: potrzebujemy krajowych zdolności cyber do skutecznego ddosowania wrogów Mama: mamy RCB-DDOS-botnet w domu #cyberbezpieczeństwo #RCB #DDoS

13377
hvg.hu Jul 28

Egy új botnet, a Dysphoria, világszerte már körülbelül 200 000 eszközt fertőzött meg, amelynek irányítási rendszere blokklánc-alapú, így nehezen észlelhető és felszámolható, és főként Telnet és SSH sebezhetőségeken keresztül terjed. #botnet #kártevő #hackertámadás

hvg.hu
Elszabadult egy új vírus, már 200 000 eszköz esett áldozatául
12438
ZEIT ONLINE Jul 16

Před volbami do zemského parlamentu v Sasku-Anhalts se objevila kampaň s falešnými zprávami, která difamuje prominentní politiky pomocí manipulativních videí imitujících seriózní média a jež podle vyšetřovatelů pravděpodobně pocházejí z ruského botnetu. #FakeNews #Wahlkampf #Desinformation

www.zeit.de
Landtagswahl Sachsen-Anhalt: Lügengrüße aus Moskau
14841
@ChrisStoecker Jul 12

Kolumne: Russlands Botnetze machen mit viel Aufwand und teils grotesker, meist justiziabler Desinformation Wahlkampf für AfD und BSW. Die Kampagnen zeigen, was Putin will - und dass alle irren, die glauben, in den sozialen Medien ein Abbild der Gesellschaft erkennen zu können. https://t.co/tpPxwttdHn #Botnetze #Desinformation #Wahlkampf #RU #DE

238
@ChrisStoecker Jul 8

Die AfD ist so sehr die Partei Putins, dass Putins Botnetze im Moment nichts anderes tun, als Wahlkampf für die AfD zu machen. Ich kann das belegen, und @dTeamUS und @antibot4navalny auch. Putin führt einen hybriden Krieg gegen Deutschland. Die AfD ist also ein Sicherheitsrisiko. #AfD #Putin #Sicherheitsrisiko #DE #RU

2140
Dnevnik.hr Jun 1

Nizozemska policija je ugasila ogromnu botnet mrežu od 17 milijuna uređaja, sumnjajući da je poslužila za prikrivanje kibernetičkih kriminalnih aktivnosti, uz podršku nizozemskog Nacionalnog centra za kibernetičku sigurnost nakon dojave istraživača. #botnet #kibernetičkaSigurnost #Rusija

dnevnik.hr
Razbijena kolosalna ruska botnet mreža od 17 milijuna uređaja, evo za što se koristila
17327
BFMTV Jun 1

Les autorités néerlandaises ont démantelé un réseau criminel de 17 millions d'appareils zombies, utilisés pour des attaques par déni de service, grâce à une opération conjointe entre la police et le Centre national de cybersécurité. #Cybersécurité #Botnets #DDoS

www.bfmtv.com
17 millions d’appareils zombies: un des plus grands réseaux de botnets, utilisé à des fins criminelles, a été démantelé par les autorités néerlandaises
18522
hvg.hu May 28

A Google, a CrowdStrike és a Shadowserver sikeresen lekapcsolta a Glassworm nevű botnetet, amely a kiberbűnözők által használt, nyílt forráskódú szoftverek fejlesztőit célzó támadások révén korábban komoly károkat okozott a digitális térben. #kiberbiztonság #hackerek #botnet

hvg.hu
Összefogott a Google két kibercéggel, majd ledobta az atomot az egyik legveszélyesebb fenyegetésre
17336
Computertrends Apr 29

Hackeři napojení na Čínu stále častěji zneužívají napadená domácí zařízení, jako jsou routery a chytré přístroje, k maskování svých kyberútoků prostřednictvím rozsáhlých proxy sítí, což představuje vážné bezpečnostní riziko a vyžaduje důkladnější monitoring a ochranná opatření. #Kyberbezpečnost #Botnety #Hackeři

www.computertrends.cz
Hackeři napojení na Čínu ke svým kyberútokům zneužívají běžná domácí zařízení - Computertrends
18588
Letem světem Applem Mar 13

Hackerům se podařilo infikovat více než 14 tisíc domácích routerů a dalších zařízení po celém světě s pomocí malwaru KadNap, čímž vytvořili decentralizovanou botnetovou síť, která je těžko zastavitelná a může být využita k DDoS útokům. Tento typ útoku je pro běžné uživatele téměř neviditelný, což zvyšuje riziko jejich zařízení. #KybernetickáBezpečnost #Malware #DDoS

www.letemsvetemapplem.eu
Tisíce routerů po celém světě padly do rukou hackerů! Vznikla tak nová kybernetická zbraň
13846