WRLD

Search

#banques
L
Le Soir 13h

Federal Minister Rob Beenders has expressed his dissatisfaction with Belgian banks that impose stricter repayment terms than legally permitted in cases of phishing and calls on them to comply with the law. #ProtectionDesConsommateurs #Phishing #BanquesBelges (translated)

www.lesoir.be
« C’est inadmissible » : un ministre fédéral s’emporte contre les banques belges
2294
La Libre.be 13h

Rob Beenders, federal minister for Consumer Protection, states that some Belgian banks impose unacceptable repayment conditions on phishing victims, in violation of the law which requires immediate compensation. #phishing #protectionsdesconsommateurs #banques (translated)

www.lalibre.be
Les banques rappelées à l'ordre par Rob Beenders : "C'est inadmissible"
2308
AlertesInfos 3d

AlertesInfos stated, citing the Ministry of Economy, that starting from November 20th, banks will need to check the financial situation of their clients before granting a new overdraft authorization, even for an amount less than €200. They would specifically examine income, expenses, and repayment capacity, and should clearly inform their clients of the cost of this facility. AlertesInfos added that the most modest households could be particularly penalized, while already authorized overdrafts would not be affected. #Economie #Banque #Finances (translated)

3473
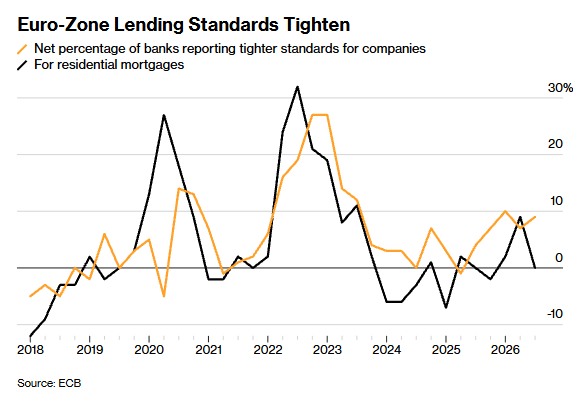
Christophe Barraud🛢🐳 5d

The author shared a Bloomberg report saying the ECB had reported that banks tightened credit conditions and saw loan demand fall. https://t.co/ud3fkKpieW https://t.co/tvv3QJoaoX #BCE #Banques #Crédit #EU

2928
Sébastien Fontenelle 1w

Fortunately, Mr. Nuñez, between two mutilations of high school students and two defamations against La France insoumise, is there to protect the congress of the party founded by SS members who wants to reappoint its president who claims that "all banks are owned by Jews." (translated)

2163
Sylvain Catherine 1w

Sylvain Catherine judged a response to his tweet to be of poor quality, considering that it already addressed most of the points raised. He particularly disputed the comparison between the France-Germany and U.S.-Germany spreads: according to him, the U.S. borrows in dollars while Germany borrows in euros. The spread between these two countries would therefore also reflect a gap in anticipated inflation — about 0.5 points higher in the U.S. over the past three years — and the policies of two distinct central banks. He noted that the Federal Reserve's key rate was between 3.75% and 4%, compared to 2.5% for the ECB. In his view, comparing France to Germany would actually neutralize these differences. Catherine also rejected the accusation that his estimate of an additional 60 billion in interest would immediately apply the cost of the spread to the entirety of the debt. He clarified that he had written that this amount "would eventually" be reached, without assuming an immediate effect. Regarding the liquidity of the French and German bond markets, he stated that both were among the most liquid. He acknowledged that the Bund constituted better collateral but believed that this was precisely because it was less risky. According to him, a liquidity gap could not explain a spread of 1.6 points and stemmed from the difference in risk between the two countries. He added that the spread did not directly correspond to a probability of default, as it combined default risk with liquidity or "convenience" premium. However, these components would nonetheless reflect the underlying risk gap between the bonds. Finally, he estimated that French bonds could benefit from the same advantages as German ones if they were equally safe and criticized the idea that the spread arose from Germany's greater perceived safety rather than the risk attributed to France. (translated)

2966
La Libre.be 2w

The recent ruling of the European Court of Justice states that banks must compensate victims of phishing for unauthorized payments within 24 hours, but Belgian banks might adopt a minimalist interpretation of this decision to limit their reimbursement obligations. #phishing #banques #remboursement (translated)

www.lalibre.be
Phishing : la récente décision de justice met-elle vraiment la pression sur les banques ?
3087
Franceinfo 2w

Google reported computer incidents affecting several of its cloud services in Europe due to a now-controlled electrical incident, leading to outages and high error rates, particularly for some British banks. #GoogleCloud #IncidentInformatique #Europe (translated)

www.franceinfo.fr
Google signale des incidents informatiques sur plusieurs services de cloud en Europe, leur rétablissement est en cours
2862
BFMTV 2w

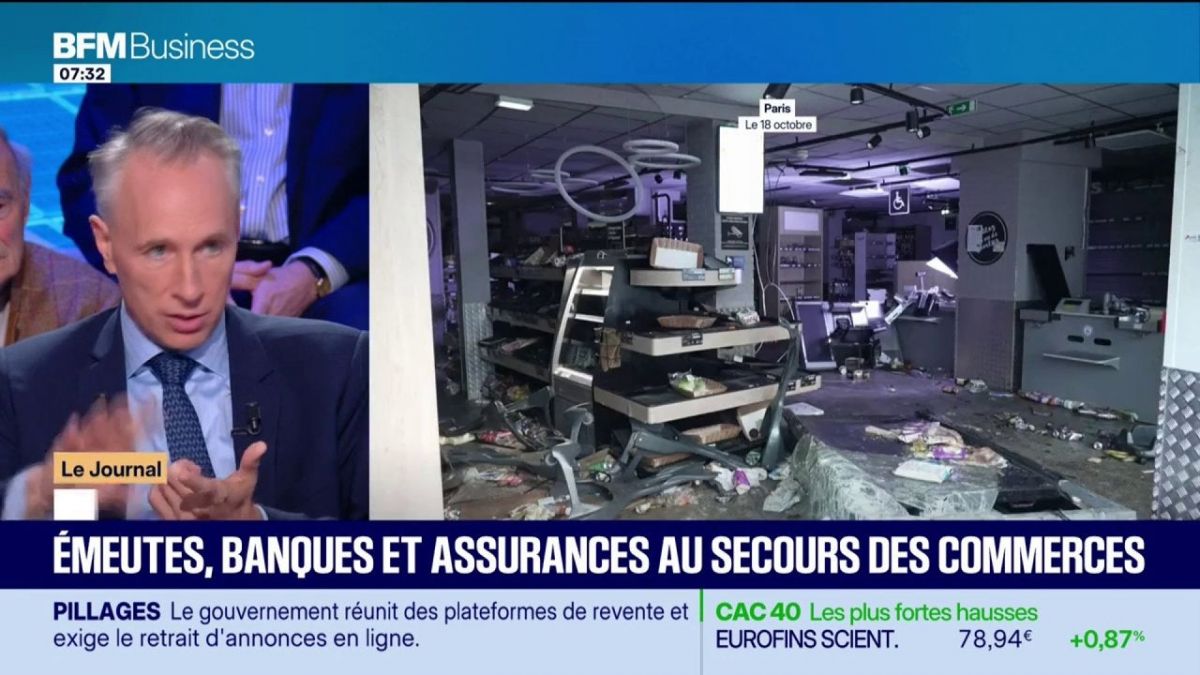
After the recent looting of 3,000 businesses, the deadline for declaring a loss is extended from 5 to 30 days, while AXA establishes a solidarity fund to support traders beyond insurance. #Banques #Assurances #Commerces (translated)

www.bfmtv.com
Banques et assurances au secours des commerces
2978
La Libre.be 2w

Since a ruling by the Court of Justice of the European Union on October 15, 2026, banks are required to immediately refund victims of phishing without being able to invoke gross negligence, and a new guide helps them recover their money in case of refusal. #phishing #sécuritébancaire #remboursement (translated)

www.lalibre.be
Victime de phishing ? Voici les nouvelles démarches pour récupérer votre argent
3439
BFMTV 2w

Half of buyers in France now borrow for 25 years, the maximum duration permitted, raising questions about the possibility of extending this duration to 30 years without risk to banks and borrowers, in a context of rising rates and increased personal contribution requirements. #immobilier #emprunt #prêt (translated)

www.bfmtv.com
La moitié des acheteurs empruntent désormais sur 25 ans, soit la durée maximale autorisée: est-il possible de repousser le curseur à 30 ans sans risque?
2870
Brèves de presse 2w

Press briefs reported that at the Motor Show, Ibrahim, a student, confronted Jordan Bardella by asking who controlled the banks and insulting him. According to the report, security immediately evacuated the student. He added that when questioned afterward, the president of the RN did not respond. https://t.co/DmVRnDXCSv #France #Politique #Auto (translated)

2991
Focus 2w

Focus reported that a visitor confronted Jordan Bardella at the Auto Show, calling him a fascist and asking him who controls the banks. https://t.co/rOf6wsI5Ua #Facho #SalonDeLAuto #Politique (translated)

2991
L
Le Soir 2w

The Court of Justice of the European Union ruled that banks must now immediately reimburse victims of online fraud, even in cases of serious negligence on their part, marking a significant change in the handling of unauthorized payments. #arnaquesenligne #CJUE #remboursement (translated)

www.lesoir.be
Union européenne : qu’est-ce qui va changer pour les victimes d’arnaques en ligne ?
3682
Cerfia 2w

Cerfia reported that the European court had decided that banks must immediately reimburse victims of unauthorized payments, including in cases of gross negligence and, on a case-by-case basis, phishing or spoofing. According to Cerfia, banks could then pursue their customers to recover the amounts if they believed that they had participated in the fraud, whether intentionally or not. The media added that it was up to the banks to prove negligence or fraud in order to obtain reimbursement of the amounts paid. #JusticeEuropéenne #Banques #Phishing (translated)

3452
SaxX ¯\_(ツ)_/¯ 2w

SaxX reported that a hacker had accessed the Danish central registry of persons, the CPR, and retrieved data associated with about 8.8 million identification numbers. According to him, these concerned living people, deceased individuals, or those who had gone abroad, and included names, addresses, and personal numbers. The author clarified that the intrusion did not directly target the Danish state, but Pays ApS, an IT company in Odense that had legal access to the registry to verify its clients' files. He indicated that the company had only two employees. Citing the newspaper Politiken, he wrote that at least three of its accounts used the password "123456", including that of the administrator. According to SaxX's account, the hacker allegedly used a leaked password from a former employee, maintained access for 21 days and 17 hours, and carried out about 14 million automated searches between September 10 and 20. The hacker also claimed that his data recovery program had been written by an AI, that he had no particular technical skills, and that he did not intend to sell or publish the data. SaxX stated that the intrusion was only discovered on October 2, after an official noticed an abnormally high bill, as searches in the registry are paid. He added that the Minister of Digital Affairs had described the incident as "deeply serious." The author also reported that the number of citizens who activated a credit fraud alert had risen from about 250,000 to nearly 970,000 in one week. According to him, the CPR had then reminded the security rules to 1,039 companies that had access to the registry, including banks, telecom operators, law firms, unions, and insurers. Finally, SaxX estimated that the incident demonstrated the risks associated with access granted to private providers, as several African states digitized their civil registries. #Cybersécurité #Hacking #Danemark (translated)

3569
Vanessa Matz 2w

Today, telecom operators have already blocked over 100 million fraudulent calls. However, new techniques, such as automated calls pretending to be your bank or Card Stop, remain difficult to detect. That is why I am currently working on strengthening our legislation to allow telecom operators, banks, and authorities to better collaborate and exchange the information necessary for detecting fraud more quickly, while ensuring the respect of privacy. #Phishing #Banques #Remboursement (translated)

Les banques devront immédiatement rembourser les victimes de phishing, même en cas de négligence : "C'est une bombe"
www.lalibre.be
3686
La Libre.be 2w

The European Court of Justice has ruled that banks must immediately (i.e., within 24 hours) compensate victims of phishing, even in cases of gross negligence, which signifies a major change for the banking sector. #Phishing #Banques #Remboursement (translated)

www.lalibre.be
Les banques devront immédiatement rembourser les victimes de phishing, même en cas de négligence : "C'est une bombe"
3686
Cerfia 3w

Cerfia, citing French breaches, listed the administrations, state services, and French public operators that may have been targeted by cyberattacks or data leaks over the past year. In the employment and social benefits sector, Cerfia reported data concerning up to 12 million employees in the URSSAF/DPAE system: names, dates of birth, employers, and hire dates. For URSSAF/Pajemploi, the figure was 1.2 million employees, with identities, addresses, social security numbers, and bank names. The census also mentioned 1.6 million young people linked to France Travail and local missions, whose identities, addresses, phone numbers, and social security numbers may have been affected. For Pass'Sport and the Ministry of Sports, it mentioned 3.5 million households along with their names, contact details, phone numbers, and addresses. It also reported nearly 1.2 million CAF/CNAF/Vacaf files claimed, without confirmation from CNAF, regarding family information, beneficiaries, and vacation stays. Cerfia also reported that Bloctel/DGCCRF had about 3 million phone numbers extracted, including 600,000 registered on Bloctel. The Agency for Services and Payment and the Coup de pouce énergie scheme may have involved 108,555 beneficiaries, with their identities, addresses, amounts of assistance, and IBANs. A link mentioned in the post referred to a service that may have affected 550,000 accounts, with names, emails, phones, dates of birth, and engagement histories. France Travail may also have been affected by agent data held by an HR service provider, while France VAE may have seen candidate data targeted. In education and training, the census reported 5.8 million DELF-DALF candidates associated with France Éducation International and GAEL, whose identities, nationalities, dates, and places of birth may have been exposed. For the Ministry of National Education, it mentioned up to 4.35 million teachers potentially affected by identity, assignment, grade, and compensation data, as well as one million students from Créteil whose personal and family data may have been exfiltrated. The COMPAS system may have involved 243,000 agents, with their names, personal addresses, and initial assignments. Up to 200,000 candidates for Ev@lang may have been affected by personal data related to language tests. Cerfia also cited ÉduConnect. The post mentioned 705,000 Parcoursup candidates in the academic region of Occitanie, whose identities, contact details, school information, scholarship status, and family data may have been affected. The intrusion was dated to October 2025. For the Ministry of Sports and FORÔMES, it advanced 450,000 candidates and identity, address, phone number, date of birth, and diploma level data. The Compte Asso was also among the mentioned services. Cerfia further reported at least 30 affected sports federations — notably in football, shooting, tennis, gymnastics, swimming, sailing, skiing, and handball — with data from license holders, including minors. At least eight public higher education institutions were cited: Angers, Lille, UMLP, Alfort, Bordeaux Sciences Agro, AgroParisTech, CNAM, and ésam. The post also mentioned the training platform of the Agency for Civic Service and the application platforms of Campus France. Among financial and administrative organizations, Cerfia reported that about 1.2 million bank accounts linked to DGFiP/FICOBA may have been affected, with identities, addresses, RIBs, and IBANs. Up to 433,485 individuals may have been impacted through the DGFiP property register, with addresses and characteristics of real estate. More than 350,000 individuals may have been affected by tax data — reference tax income, family quotients, and withholding rates — and the portal for vacant inheritances was also listed. For DGAFP/Choosing Public Service, the figure mentioned was 377,418 candidates, with their identities, contact details, diplomas, and professional backgrounds. The post also cited the Ministry of the Interior and the TAJ, FPR, SIA, and SIV files. The census mentioned 774,000 people linked to Cnous/CROUS, with identities, emails, and appointments. It also reported 329,000 extracted documents concerning 139,000 individuals, including identity and income verification documents. ANFR/Radiomaritime may have concerned 330,000 users and their identities, addresses, emails, phones, and dates of birth. For INSEE, Cerfia reported 12,800 agents and former agents, with identities and professional contact details. The Institute for Research and Development may have involved about 7,500 individuals, with identity, address, and professional data along with, for some, social security numbers; exfiltration was not confirmed. The post also cited CNRS and personnel data. Cerfia indicated that Public Health France and a service provider may have been involved for about 80,000 contacts: names, emails, addresses, and professional phones, without any reported medical data. For Tracfin and a support provider, it mentioned 136 professionals, their identities and contact details, as well as 213 assistance requests; according to ANSSI, no suspicion declarations were reported. ANSSI and its innovation laboratory were also listed, with 118 Metabase accounts potentially affected by a compromise. The post further cited 70,000 files and 160,000 administrative documents that may have been exfiltrated from DINUM/HubEE, some containing personal data, as well as the State Cloud. More than 30,000 individuals may have been affected by directory, identity, and professional contact data related to AEFE/Orion. At the Ministry of Ecological Transition, 22,000 agents and accredited organizations may have been involved with access to personal data, and over 300 email accounts may have been compromised. Cerfia also mentioned messaging services and a server from the General Directorate of Customs and Indirect Rights, as well as Tchap, the secure messaging service of the State. Finally, the census reported 14 SDIS targeted, with personal and professional data, internal documents, and medical data. At least five hospital establishments may have been affected: AP-HP, Hospices Civils de Lyon, as well as the establishments in Perpignan, Chaumont, and Haute-Comté. The list also included the French Office for Biodiversity and hunting permits, the National Library of France, and the Center for National Monuments through a ticketing service provider, regional health agencies and vaccination data, as well as the French Office for Immigration and Integration and an IT service provider. #Cyberattaques #ProtectionDesDonnées #SécuritéInformatique (translated)

3691
BFMTV 3w

In Lyon, eight banks and two insurance agencies were vandalized during high school protests demanding increased funding for education, with participants estimated between 480,000 and 161,500. #MouvementLycéen #Manifestation #Éducation (translated)

www.bfmtv.com
À Lyon, huit banques et deux agences d'assurance dégradées en marge du mouvement lycéen à Lyon
2653